
Worm Redux: Fresh Mini Shai-Hulud Infections Bite Supply Chain
Hundreds of npm packages infected by the self-propagating, credential-stealing worm from TeamPCP are related to the open source TanStack ecosystem.
Aggregated from vendor advisories, security research, and industry publications.
Hundreds of npm packages infected by the self-propagating, credential-stealing worm from TeamPCP are related to the open source TanStack ecosystem.
Hundreds of packages across npm and PyPI have been compromised in a new Shai-Hulud supply-chain campaign delivering credential-stealing malware targeting developers. [...]
Curl’s lead developer says Mythos claims are marketing, but many in the industry believe the results stem from Curl’s robust security. The post Claude Mythos Finds Only One Curl Vu…
This is the worst Linux vulnerability in years. TL;DR copy.fail is a Linux kernel local privilege escalation, not a browser or clipboard attack. Disclosed by Theori on 29 April 20…
SAP has released the May 2026 security updates addressing 15 vulnerabilities across multiple products, including two critical flaws in the Commerce Cloud enterprise-grade e-commerc…
Many AI-first enterprises have already embraced sovereign architectures for general AI initiatives; cybersecurity—and the SOC—should be next. The post Is the SOC Obsolete, and We J…
It looks like you're trying to get more Microsoft 365 users to engage with your assistant. Would you like help?

Agentic AI is already running in production environments across many organizations today. It is executing tasks, consuming data, and taking actions — most likely without meaningful…
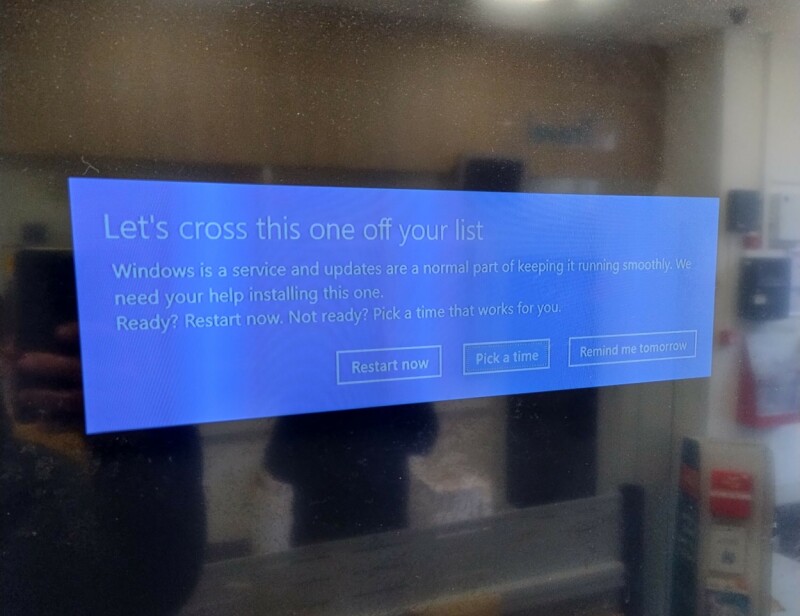
Customers left staring at restart plea with no keyboard, mouse, or hope
Over 400 malicious versions of 170 packages were published as part of the new Mini Shai-Hulud campaign. The post TanStack, Mistral AI, UiPath Hit in Fresh Supply Chain Attack appea…
After years of stopping dead at the green bubble border, iPhone and Android users can finally send E2EE messages without relying on third-party apps
Instructure, the edtech giant behind the widely popular Canvas learning management system (LMS), has reached an "agreement" with the ShinyHunters extortion group to prevent the dat…
Device delivers smoother streaming and simpler interaction, elevating home entertainment
A month after bringing systems back online, SaaS vendor tells customers attackers potentially walked off with operational data, contact details, and payroll numbers

TeamPCP, the threat actor behind the recentsupply chain attack spree, has been linked to the compromise of the npm and PyPI packages from TanStack, UiPath, Mistral AI, OpenSearch, …
Satellite service supports troops and Ukraine, but payments may raise eyebrows after boss's political broadsides

American educational technology company Instructure, the parent company of Canvas, said it reached an "agreement" with a decentralized cybercrime extortion group after it breached …

OpenAI has launched Daybreak, a new cybersecurity initiative that brings together frontier artificial intelligence (AI) model capabilities and Codex Security to help organizations …
Fears exponential increase in attack scale and speed

Apple on Monday officially released iOS 26.5 with support for end-to-end encryption (E2EE) to Rich Communication Services (RCS) in beta as part of a "cross-industry effort" to repl…
Critics are not convinced this plan to add an ‘area code’ based on ASNs has much merit
Code hosting biz is trimming its global footprint and flattening its management layer

Linux server admins may get the ability to turn off a vulnerable function in the OS kernel until a patch for a zero-day vulnerability is ready, if a proposal from a kernel develope…
Orbital compute platform, which launched on a mission to the ISS last year, gets an immutable upgrade alongside refreshed container images
Join us to learn how to architect a development environment where your builders and their agents can move fast and securely.
Analyst says modernizing applications is probably a better use of your time than hypervisor migration
UPDATED: Sorry, kids, everything's back up so get to work on your new assignment - An essay on the ethics of paying ransoms, because it looks like that's what happened here
California Attorney General Rob Bonta announced a proposed $12.75 million settlement agreement with General Motors (GM) over allegations that the company violated the California Co…
Checkmarx warned over the weekend that a rogue version of its Jenkins Application Security Testing (AST) plugin had been published on the Jenkins Marketplace. [...]
A security researcher has released a proof-of-concept tool named GhostLock that demonstrates how a legitimate Windows file API can be abused in attacks to block access to files sto…