Security & Lifecycle News
Aggregated from vendor advisories, security research, and industry publications.
1Password Teams With OpenAI to Stop AI Coding Agents From Leaking Credentials
1Password says AI coding agents should never hold persistent secrets, introducing a just-in-time credential model for OpenAI Codex designed to keep credentials out of prompts, code…
Those spared latest Meta job cuts forcibly reassigned to AI roles
Staff protest overhaul and mouse tracking at 'Employee Data Extraction Factory'
Anthropic Silently Patches Claude Code Sandbox Bypass
The researcher who found it says the vulnerability could have been chained with a prompt injection to exfiltrate data. The post Anthropic Silently Patches Claude Code Sandbox Bypas…
Drupal critical update to fix bug with high exploitation risk
Drupal has announced a "core security release" scheduled for later today, warning that threat actors might develop exploits within hours of the update disclosure. [...]

Webworm Deploys EchoCreep and GraphWorm Backdoors Using Discord and MS Graph API
Cybersecurity researchers have flagged fresh activity from a China-aligned threat actor known as Webworm in 2025, deploying custom backdoors that employ Discord and Microsoft Graph…
Datacenter builds could be shielded from judicial review in UK planning reforms
British government wants to ensure no hold-ups for critical energy and infrastructure projects
Microsoft says cu l8r to text message security
Old, busted, insecure authentication to be replaced with something shinier and safer
'Workforce rebalancing' comes for Kyndryl, and delivery teams are in the firing line
Big Blue spinout eyes up to $500M in savings and agentic AI while insiders grumble it's still 'IBM without the hardware'
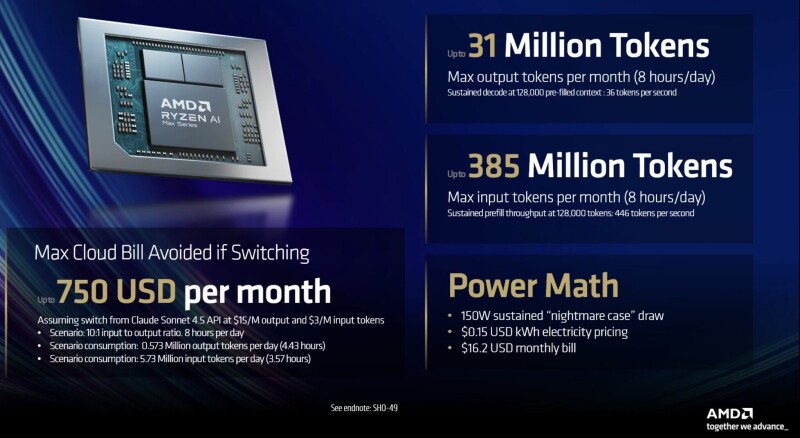
AMD says its $4K Ryzen AI Halo workstation practically pays for itself
Assuming you’re vibe coding for 8 hours a day, that is

Agent AI is Coming. Are You Ready?
New Industry Data Just Released Suggests Not. On May 19th, 2026, Orchid Security released the results of our Identity Gap: Snapshot 2026. Among the findings, "identity dark matter…
ESA boss tires of being dragged around by NASA mood swings
Are we pilots or are we passengers? Aschbacher asks
Over 320 NPM Packages Hit by Fresh Mini Shai-Hulud Supply Chain Attack
A compromised maintainer account was used to publish malicious package versions across the @antv namespace. The post Over 320 NPM Packages Hit by Fresh Mini Shai-Hulud Supply Chain…
Caught Off Guard: Securing AI After It Hits Production
As enterprises rush AI projects into production, security teams are increasingly being forced into reactive mode. The post Caught Off Guard: Securing AI After It Hits Production ap…
Exploit released for new PinTheft Arch Linux root escalation flaw
PinTheft, a recently patched Linux privilege escalation vulnerability, now has a publicly available proof-of-concept (PoC) exploit that allows local attackers to gain root privileg…

Typosquatting Is No Longer a User Problem. It's a Supply Chain Problem
AI-generated lookalike domains are now embedded inside the third-party scripts running on your web properties. Here's why your current stack can't see them, and what detection actu…
GitHub says internal repos exfiltrated after poisoned VS Code extension attack
Initial assessment says customer data spared while users wonder what else may have slipped out
Real-World ICS Security Tales From the Trenches
SecurityWeek spoke with several ICS security experts and companies about their most memorable experiences in the field. The post Real-World ICS Security Tales From the Trenches app…
Virtual Event Today: Threat Detection & Incident Response Summit
Don't miss this virtual event as we explore how to cut through alert fatigue, leverage AI and unified platforms to accelerate investigations, and apply actionable threat intelligen…
Smaller suppliers invited to pitch for £2.9B UK defense tech framework
Government Commercial Agency wants DIPS 2 to reach beyond MoD buyers and the usual big-name suppliers
GitHub Confirms Hack Impacting 3,800 Internal Repositories
The TeamPCP hacking group accessed the repositories after a GitHub employee installed a poisoned VS Code extension. The post GitHub Confirms Hack Impacting 3,800 Internal Repositor…
PostgreSQL backup tool gets some backup of its own after sole maintainer sounds alarm
AWS, Percona, Supabase, pgEdge, and Tiger Data rally round pgBackRest with funding pledge
London's police asked Big Tech for comms data over 700,000 times last year
A Freedom of Information Act request shows the extent of the surveillance

Microsoft Releases Mitigation for YellowKey BitLocker Bypass CVE-2026-45585 Exploit
Microsoft on Tuesday released a mitigation for a BitLocker bypass vulnerability named YellowKey following its public disclosure last week. The zero-day flaw, now tracked as CVE-20…
ZTE releases Sustainability Report 2025: driving a new chapter in sustainable development through AI
Through its "All in AI, AI for All" vision, ZTE surpasses climate targets, bridges the global digital divide, and strengthens governance resilience
GitHub confirms breach of 3,800 repos via malicious VSCode extension
GitHub has confirmed that roughly 3,800 internal repositories were breached after one of its employees installed a malicious VS Code extension. [...]
Microsoft shares mitigation for YellowKey Windows zero-day
Microsoft has shared mitigations for YellowKey, a recently disclosed Windows BitLocker zero-day vulnerability that grants access to protected drives. [...]
Interpol's 'Operation Ramz' Pioneers Cross-Region Collabs in Middle East
While the numbers are modest, the crackdown on cybercrime involved 13 countries in the MENA region, the largest law enforcement collaboration to date.
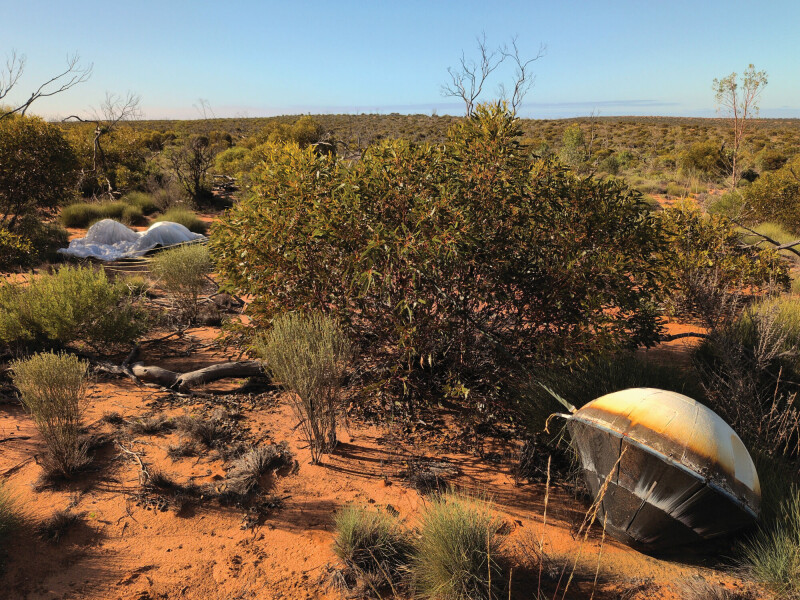
Space factories edge closer after experimental capsule survives hypersonic landing
Varda hails success of autonomous touchdown tech and celebrates heat data haul

Grafana GitHub Breach Exposes Source Code via TanStack npm Attack
Grafana Labs, on May 19, 2026, said an investigation into its recent breach found no evidence of customer production systems or operations being compromised. It said the scope of …