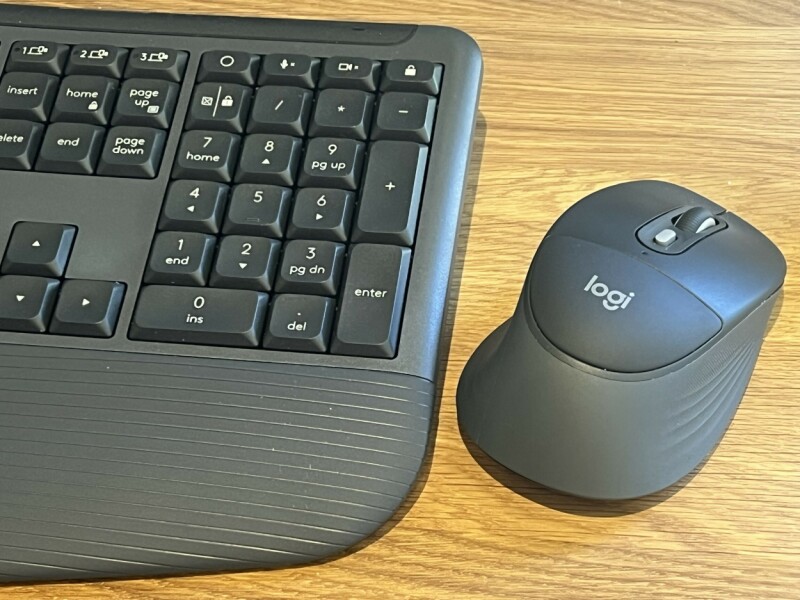
Logitech unveils a cushioned mouse for all-day use
Ideal for aching palms – though only if you're right-handed
Aggregated from vendor advisories, security research, and industry publications.
Ideal for aching palms – though only if you're right-handed
Hardcoded machineKey values in a configuration file enabled ViewState deserialization attacks leading to remote code execution. The post Hackers Exploited KnowledgeDeliver Zero-Day…
Register to enjoy free access and explore the tools, strategies, and frameworks needed to build a resilient security program for a world where every minute counts. The post Watch o…
DockSec, an OWASP incubator project, correlates findings from multiple container security scanners and uses AI to generate plain-English remediation guidance and exact Dockerfile f…
Britain's 'free' internet economy is powered by invisible data extraction that feeds advertisers, AI firms, and digital platforms

Multi-factor authentication (MFA) was supposed to close a critical gap in identity security. It meant that, even if an attacker possessed the account credentials, they couldn't log…
Lithuanian authorities are on high alert after a massive data leak involving more than 600,000 entries from national data registers. The post Lithuania Suspects Foreign Involvement…
Network-wide rollout boosts energy efficiency by 10.6%, cutting carbon emissions and operational costs without compromising user experience
AI coding agents may make software cheaper to build, but switching off major platforms remains expensive and risky
The two own Dutch companies that allegedly provided bulletproof hosting services to Russia-aligned threat actors. The post Admins of Bulletproof Hosting Service Used by Russian Hac…
Internal notes point to cloud connectivity woes for older OfficeJets, though company denies systemic issue

The Indian Computer Emergency Response Team (CERT-In) has issued new guidelines requiring organizations to patch critical security vulnerabilities in internet-exposed systems withi…
https://arstechnica.com/information-technology/2026/05/milli... Comments URL: https://news.ycombinator.com/item?id=48277107 Points: 126 # Comments: 51
CISA has given U.S. government agencies until Wednesday evening to secure their servers against an SQL injection vulnerability in the Drupal content management system (CMS) that it…
DIY or die. Just don't let the CIA buy it
Microsoft has confirmed a new known issue affecting Windows Server 2016 systems that causes domain controller lookups to fail after installing the KB5087537 May 2026 security updat…

The Iranian state-sponsored threat actor known as Nimbus Manticore (aka Screening Serpens and UNC1549) has been attributed to a fresh campaign using lures impersonating organizatio…
The ShinyHunters extortion gang stole the personal information of over 183,000 people after hacking the systems of convenience store chain giant 7-Eleven in April, according to dat…
CEO jumps on the ‘We must be fit for the AI future’ bandwagon

A now-patched high-severity security flaw affecting Digital Knowledge KnowledgeDeliver, a Learning Management System (LMS) popular in Japan, was exploited as a zero-day to deliver …
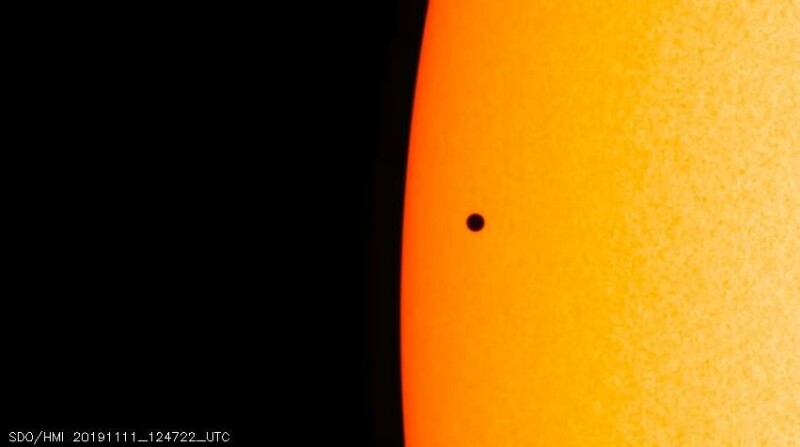
Due on November 21, eleven months late - but on time to do science!
Worries change may be ‘governed only by technocratic thinking and presented as necessary and inevitable’
Article URL: https://support.apple.com/en-us/127115 Comments URL: https://news.ycombinator.com/item?id=48273169 Points: 172 # Comments: 114
Anthropic appears to be preparing for the public rollout of the Mythos model, which was announced in April as a restricted model that poses major security risks to private and publ…

Monday recap. Same mess, new week. A sketchy dev tool got people pwned, old bugs came back from the dead, and security products somehow needed protecting from themselves. A bunch …
Sites belonging to major universities such as Harvard and Oxford, as well as DuckDuckGo, have been compromised in the attack. The post Ghost CMS Vulnerability Exploited to Hack Ove…
Authorities in the Netherlands have arrested the co-owners of two related Internet hosting companies for operating IT infrastructure used by Russia to carry out cyberattacks, influ…
The FBI is warning about the Kali365 phishing-as-a-service platform (PhaaS) that is used to hijack Microsoft 365 accounts by abusing OAuth device code authentication to steal sessi…
Google Search used to direct users to websites; AI Mode will keep them in Google's garden
The affected third-party vendor has not been named, but one possible candidate is TriZetto. The post Oncology Institute Discloses Data Breach appeared first on SecurityWeek.