Europe's new import rules are coming for your bargains
Good news if you're an OEM printer maker, EU retail biz, or a customs official... but hobbyists and others less pleased
Aggregated from vendor advisories, security research, and industry publications.
Good news if you're an OEM printer maker, EU retail biz, or a customs official... but hobbyists and others less pleased
Attackers are now exploiting a maximum-severity Adobe ColdFusion vulnerability tracked as CVE-2026-48282, according to vulnerability intelligence company KEVIntel. [...]
The PolinRider campaign has compromised more than 100 legitimate open source packages and repositories to deliver a backdoor and information stealer to developers. The post North K…

With all of the attention being paid to the compute resources required to power AI, connectivity is sometimes overlooked. This poses a new dynamic for those planning their next pha…

A streaming box should not need a threat model. Neither should a username field, a demo repo, a reset flow, or a browser permission prompt. That is the irritating part this week: t…
Oracle's down more than 40% this month, the BIS thinks AI could destroy the economy, and we've got the Kettle on for a chat about the whole mess
Organizations are urged to patch after proof-of-concept code makes the Linux root escalation flaw easier to exploit. The post Proof-of-Concept Exploit Released for Linux ‘Bad Epoll…
Up to 150 more stores to get the 'Orwellian' tech by year's end

Building a shortlist for an AI SOC evaluation can be tough. SIEM, SOAR, and pureplay AI SOC vendors are all saying the same thing. But behind the identical label sit very different…
Researchers uncovered two campaigns embedding indirect prompt injections in malicious websites to exploit autonomous AI agents browsing the web. The post Prompt Injection Attacks T…

A suspected China-nexus threat activity cluster has been observed targeting Indian taxpayers, tax professionals, and corporate finance teams to deliver a remote access trojan desig…
ShinyHunters leaks names, addresses, DOBs, and more after Christian college discloses cyberattack
France is accelerating its transition to post-quantum encryption: France’s cybersecurity agency ANSSI said on Tuesday it would stop certifying security products that lack quantum-r…
Article URL: https://www.map.signalbox.io Comments URL: https://news.ycombinator.com/item?id=48802535 Points: 414 # Comments: 155
Modula-based source code resurfaces after nearly four decades

Researchers at Shandong University have shown a fast new way to pull data off computers that are cut off from every network. The technique, called TrojPix, tweaks on-screen pixels …
Barney Rubble points to bubble trouble

Cybersecurity researchers have flagged a novel Java-based remote access trojan (RAT) called QuimaRAT that's capable of targeting Windows, Linux, and macOS environments. According …
Who wrote this rubbish? Oh ...

Researchers found a flaw in Opera GX, the gaming-focused version of the Opera browser, that let a malicious website silently install a browser add-on and use it to lift specific da…

Scanners meant to catch malicious add-on "skills" for AI coding agents can be fooled by a few simple changes that leave the malware working, according to a new study from researche…
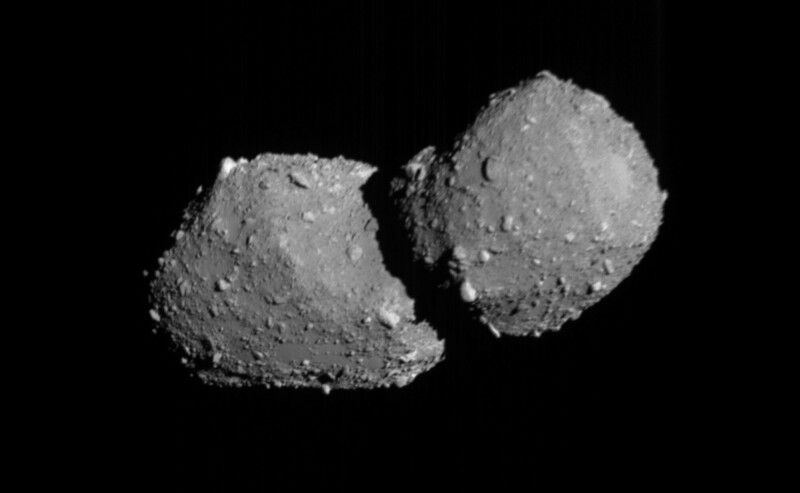
Zipped just 800m past Asteroid Torifune as part of very extended mission - and sent back a pic, too
SCO's legal successor Xinuos asks legal brains to let it bite IBM over ancient license and copyright claims
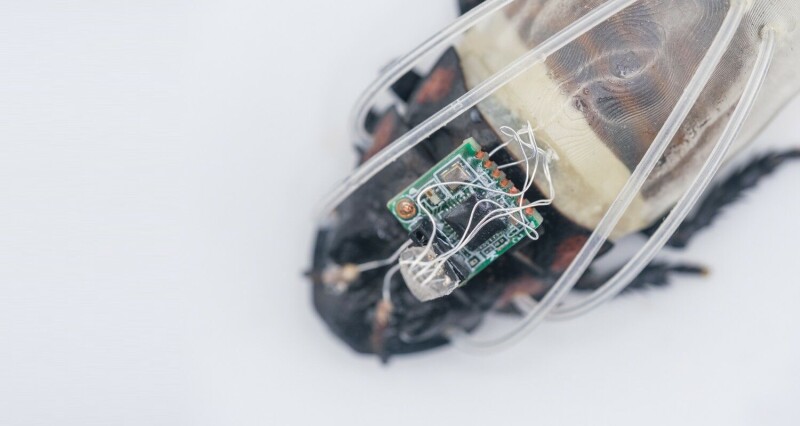
PLUS: India attacks Uber; South Korea warned AI boom is dangerous; Scuba-diving cyborg cockroach; and more!
Financial institutions are putting their clients at risk in the name of convenience.
Flipper Devices says development of the Flipper Zero firmware will continue, albeit with a smaller internal team and greater reliance on community contributions. [...]
Prepare to be befuddled and bamboozled – and probably bewitched
Researchers identified what they believe is the first documented case of a ransomware operation, JadePuffer, conducted entirely by a large language model (LLM) agent. [...]

A U.S. government entity paid about $1 million to keep stolen files from being leaked, according to a new case study by Rakesh Krishnan for Ransom-ISAC, built on a leaked negotiati…

The North Korean threat actors linked to the Contagious Interview campaign have been observed publishing 108 unique packages and web browser extensions spanning npm, Packagist, Go,…