Russian spies turn public Wi-Fi into malware delivery systems
Keyloggers, audio-visual surveillance, and token theft on CaptivePortal's agenda as hospitality sector put on alert
Aggregated from vendor advisories, security research, and industry publications.
Keyloggers, audio-visual surveillance, and token theft on CaptivePortal's agenda as hospitality sector put on alert
The payments giant says BioCatch’s behavioral and device intelligence will help financial institutions combat account takeovers, scams and other forms of digital fraud. The post Vi…
The list of people behind companies, foundations and trusteeships is part of efforts to combat money laundering and terror financing. The post Cyberattack Hits Liechtenstein’s Regi…
A cyberattack on the U.K.'s Police National Legal Database (PNLD) has compromised contact data of more than 100,000 police officers and other criminal justice professionals. [...]
Flare researchers analyzed thousands of underground posts to examine how the BTMOB Android malware operation evolved into a fragmented ecosystem of resellers, source-code vendors, …
Taiwanese silicon biz believes it can take up to 20% of $80B market with upcoming ASIC chips, but analysts are sceptical
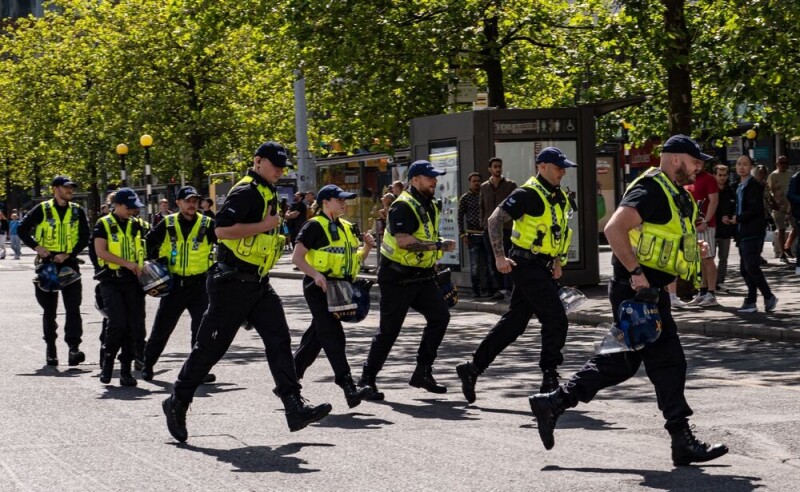
ExfilSquad claims 135,000 contact records weeks after hitting the Department for Education

This week kept coming back to permission. A model crossed a boundary. A wallet trusted bad randomness. Webmail kept an intruder around. Public systems, package feeds, hotel network…
Accountability without any real authority is driving CISO burnout, and organizations need to take notice.
Turning two Mars testbeds into one lunar explorer may prove anything but cheap
Trump rejects Tehran theory, blames 'grossly incompetent' governor of Minnesota instead
The bank holding company was hacked in June, but the investigation into the incident continues. The post River Bank Says Hackers Deleted Data Stolen in Ransomware Attack appeared f…
Venture financing has become an essential factor in growing new business in today’s fast moving economy. Horizon3’s latest funding explains how and why. The post Horizon3 Raises $2…
Turns out letting anyone rewrite the planet with a prompt had drawbacks
Cato Networks has expanded the AI capabilities of its cloud-based secure access service edge (SASE) platform with Agentic Threat Prevention. This new service uses AI agents to pred…
The N‑central vulnerability CVE-2026-18577 has been exploited in the wild after threat actors found a patch bypass. The post N‑able Patches Vulnerability Exploited to Hack N-centra…
Weird times in earnings-land, and we're talking about it on The Reg's home grown podcast
The physical security firm says its alarm monitoring and system functionality have not been affected. The post Brinks Home Discloses Data Breach as Hackers Leak Files appeared firs…

AI is moving incredibly fast, and every security leader is feeling the pressure to keep up. AI platforms like Claude, Codex and Cursor are already helping security teams write det…
Article URL: https://research.jfrog.com/post/sqlite-critical-cves-or-llm-slops/ Comments URL: https://news.ycombinator.com/item?id=49154332 Points: 588 # Comments: 215
Employee failed to follow security policy, leaving internal management file open to the public

An unknown Chinese-speaking threat actor has been observed running a campaign targeting Apple iOS devices by leveraging a publicly leaked version of the DarkSword exploit kit. Att…
This essay originally appeared in Foreign Policy. Earlier this month, two of OpenAI’s models broke out of their containment sandbox and attacked another AI company. The story is ki…
The INC Ransomware gang has been targeting vulnerable SMA1000 appliances for root access and lateral movement. The post Recent SonicWall Vulnerabilities Exploited in Ransomware Att…
LLMs are theft by 'absolute scum' who make life harder for writers by putting them in copyright peril
Midnight Blizzard has been stealing Microsoft account credentials via compromised Wi-Fi networks at hospitality organizations. The post Russian State APT Linked to Recent Public Wi…
Use it to debug and review, says Big Red, but don't submit its output

The Police National Legal Database (PNLD) has confirmed that police, government and customer contact information was compromised and published on the dark web. The data included n…
Michigan, South Dakota, and Georgia are reportedly on the list of states whose water systems have been targeted by Iran-linked hackers. The post US Water Cyberattacks Extend Beyond…
'As a big AI skeptic, you just blew my mind'