Security & Lifecycle News
Aggregated from vendor advisories, security research, and industry publications.
Friday Squid Blogging: Arctic Bobtail Squid Video
Nice video of the Arctic bobtail squid. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation policy.
Metabase SQLi zero-day exploited in customer data-theft attacks
A critical Metabase SQL injection vulnerability was exploited in zero-day attacks to breach customer instances in data theft attacks, known to impact Framework and Tally. [...]
Unlimited Technology Systems breach impacts 3.8 million people
Healthcare software company Unlimited Technology Systems reported that more than 3.8 million people were impacted by a data breach incident that occurred in October 2025. [...]
AI titans to tidy agent frontier with plugin prescription
Agent Plugins 1.0 defines a write-once-run-anywhere container for passing tools and skills across different agent platforms

Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targeting Windows, Mac, and L…

ClickFix Attacks Deliver macOS Stealer That Can Drain Crypto Wallets
ClickFix-style attacks are being used to deliver a Go-based malware capable of stealing cryptocurrency assets, as well as browser-stored passwords, Apple iCloud Keychain data, and …
HN837: Agentic AI to Reduce MTTR
Ethan Banks sits down with Eduard Dulharu live at AutoCon 5 to explore how agentic AI can be used to reduce Mean Time to Recovery (MTTR) for complex network environments. Eduard br…

UNC6671 Vishing Attacks Target Personal Phones to Steal SaaS Data
A recent wave of cyber attacks targeting financial services, private equity, and professional services has been attributed to a data extortion group known as UNC6671. "UNC6671 con…
AI-Generated Patches Fail Half the Time
A study of more than 6,000 patches found that even working patches can introduce new bugs, break something else, or are open to bypass.
Ransomware attacks spike as world distracted by AI
What, you didn't think the top gangs were busy watching agents escape their sandboxes too, did you?
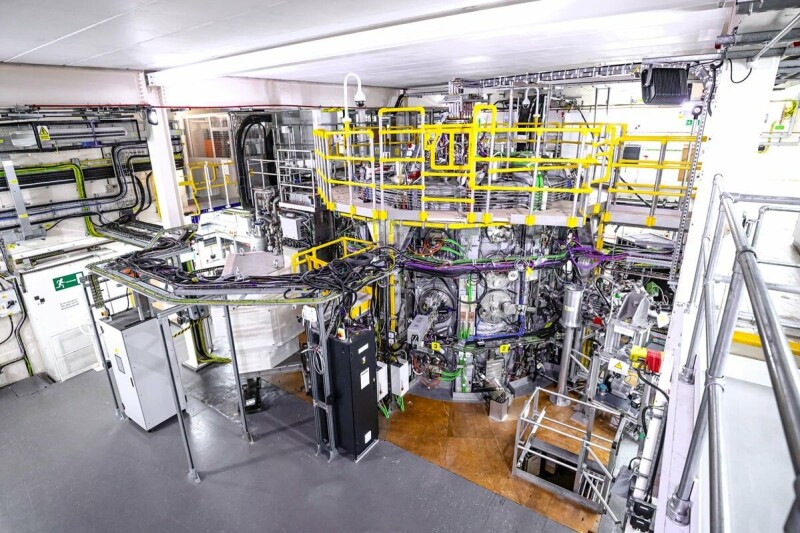
Brit boffins boast of beating barriers to building fusion power
MAST Upgrade installation hit highest pressure ever achieved without the super-hot plasma destabilizing
Samsung offers future AI memory roadmap
Samsung Electronics has unveiled a trio of next-generation memory technologies aimed at overcoming the performance, power and capacity limitations facing artificial intelligence in…
Levi Strauss & Co. says hackers stole corporate data in cyberattack
Levi Strauss & Co. (Levi's) says that hackers used social engineering on three of its employees to gain access to and steal corporate data stored on their machines. [...]
Polish data center plans to send its waste heat to the neighbors
As Europe swelters in a heatwave, residents probably don’t want to hear about ways to make their homes even hotter, but that’s what Polish property developer Citylink is talking ab…
N-able God mode flaw: Vendor confirms attackers reached customer networks as second hotfix lands
Attackers turned admin access into a route downstream, while N-able tells N-central customers to patch – again
ShinyHunters called cancer diagnostics biz and tricked staffers into giving them access. Now they've dumped 10.9M email addresses
Cancer diagnostics breach spills personal and health info as extortion crew says healthcare giant ‘should’ve paid the ransom’
In Other News: AI Slop Limits Apple Bounties, North Carolina Port Attacks, Hackers Target Wall Street
Noteworthy stories that might have slipped under the radar: ban on Chinese data center tech, QuickFox VPN supply chain attack, IEH Corporation mailbox breached via phishing. The po…
MIT boffins' TONTOU attack slips through Spectre defenses on Intel and AMD CPUs
Timer interrupts reopen branch predictor poisoning window, with a working Zen 2 exploit to prove it
Real emails, hijacked payments: Two H1 2026 attack chains
Gen's H1 2026 Threat Report examines two separate attack chains. One used compromised business inboxes and browser manipulation in a banking-malware campaign, while the other used …
Scot NHS trust probes access to medical records of 9-year-old girl after man arrested on suspicion of murder
Investigation into whether staff improperly accessed Minnie Merriman’s file after she was named for the first time this week
North Carolina Ports confirms cyberattack disrupting operations
The North Carolina Ports Authority has confirmed that a cyberattack disrupted IT systems and slowed operations at Port of Wilmington, Port of Morehead City, and Charlotte Inland Po…

New WordPress Pre-Auth XSS Could Lead to PHP Code Execution - Patch ASAP
WordPress has fixed a pre-authentication reflected cross-site scripting (XSS) flaw in its login screen that affects every version of the content management system. pwn.ai demonstra…
Microsoft tosses Teams Live chat into its feature graveyard
Website support widget lasted 18 months before Redmond ended the conversation

Growing Up The Hard Way
Open Source had a great childhood. For two decades it got to be a kid. It ran around barefoot, gave everything away, trusted strangers, and never once thought about who was watchi…
Attacker phished way into US defense supplier's Microsoft 365 account
Intruder gained access to engineering files and potentially export-controlled technical data

18-Year-Old Linux SCTP Flaw Could Let Local Users Gain Root and Escape Containers
A use-after-free bug in Linux's SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to escape a container and reach the machine un…
AMD to buy Taalas, maker of model-specific AI chips for enterprise inference
As enterprises look for ways to cut the cost of running AI models in production, AMD is betting that not every AI workload will be best served by a power-hungry general-purpose GPU…
Vishing Extortion Group UNC6671 Rebrands After Making Millions
Initially calling itself BlackFile, the group has expanded operations to the Redact, Pink, Helix, and Falcon brands. The post Vishing Extortion Group UNC6671 Rebrands After Making …
Intrusion at US healthcare software provider puts 3.8M people's data at risk
Unlimited Technology Systems says names, Social Security numbers, diagnoses, and insurance details may have been swiped