The Gentlemen come calling as Nutex confirms sensitive data theft
Ransomware crew threatens publication while healthcare biz assesses which records escaped
Aggregated from vendor advisories, security research, and industry publications.
Ransomware crew threatens publication while healthcare biz assesses which records escaped
Nearly 22,000 Microsoft Exchange servers exposed online remain unpatched against a high-severity authentication bypass vulnerability that allows attackers to hijack all user mailbo…
Forescout researchers used Claude AI to port a remote code execution exploit between WAGO PLC models. The post Experiment: Porting a PLC Exploit With AI Takes Hours and Hundreds of…
Tracked as CVE-2026-0768, the security defect allows unauthenticated attackers to execute arbitrary Python code remotely. The post Hackers Start Exploiting Critical Langflow Vulner…
Hosting software vendor tells customers to reset credentials and hunt for malicious packages

The most common way into a company last year was to ask. A web page tells the visitor to prove they are not a robot. While they read the instructions, it quietly places a command …
The defendants unsuccessfully attempted to physically install malware on ATMs to force them to dispense cash. The post Five Venezuelans Plead Guilty in US Court to ATM Jackpotting …
August 27 update reportedly scrambles cursor customizations as bogus antivirus alerts spread
The company has notified the SEC that hackers accessed patient, employee, provider, business, and financial information. The post Ransomware Gang Claims Nutex Health Data Breach ap…
And no sharing your allowance! What do you think we are, communists?
Dutch in-process OLAP systems set to be the 'SDK for data' as developers scale systems, cloud giant claims after DuckLab acquisition
Exploitation of the authentication bypass vulnerability CVE-2026-82329 started just days after its public disclosure. The post Critical JFrog Artifactory Vulnerability Reportedly E…
Nathan E. Sanders and I are writing a series of essays on real-world examples of democratic technologies for The Renovator. I haven’t been posting the full text on the blog because…
A China-linked cyber espionage group has expanded beyond VMware environments to target network and authentication infrastructure that enterprises rely on to manage access and admin…
Five Venezuelan nationals pleaded guilty to attempting to empty automated teller machines (ATMs) using malware in a series of ATM jackpotting attacks. [...]
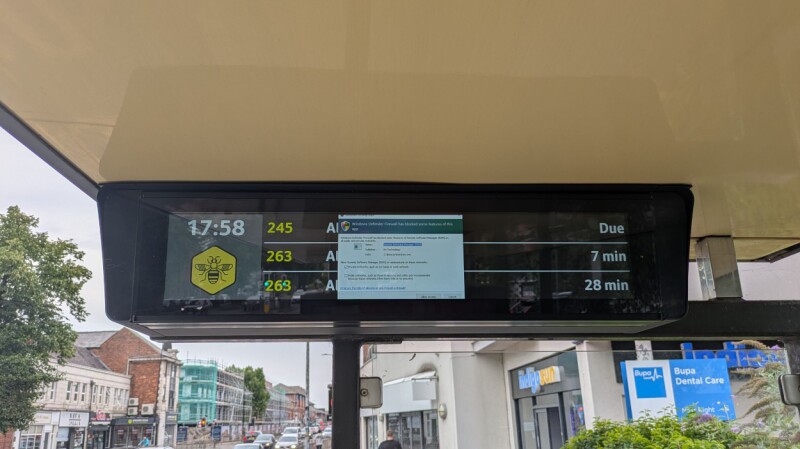
Or possibly "AI", it's hard to tell behind the firewall warning
Hackers stole personal and health information from the healthcare technology company’s AWS infrastructure. The post 9.5 Million Impacted by Aesto Health Data Breach appeared first …

METR (short for Model Evaluation and Threat Research and pronounced "Meter"), a research non-profit that evaluates frontier artificial intelligence (AI) models for their ability to…
Three critical issues in the Fireware OS iked process could allow unauthenticated attackers to execute arbitrary code remotely. The post WatchGuard Patches Critical Vulnerabilities…
Hacking education to thrive in the AI world is the first and best step in keeping control

Cybersecurity researchers have disclosed a new technique dubbed GuardBreaker that's been put to use by a Russia-aligned threat actor known as UAC-0099 against a target in Ukraine w…
Two security vulnerabilities in the PaperCut NG and MF print management software, patched last week after being exploited as zero-days, are now being abused in data theft attacks. …

Threat actors are exploiting two critical flaws impacting Langflow and Ruby on Rails, according to new findings from VulnCheck. The vulnerabilities in question are listed below - …
CISA has added the vulnerabilities tracked as CVE-2026-82078 and CVE-2026-81578 to its KEV catalog. The post PaperCut Exploitation Escalates to Active Intrusions appeared first on …
Virtzilla finding more ways to pull data out of DRAM to enable ‘densification’ and dodge the RAMpocalypse
GenAI now reaches 80% of occupations, but in most of those fewer than half of workers use it
Even when you think you're not buying Nvidia, you might still be buying Nvidia
McKesson admits breach as ShinyHunters demands $55.2M
A threat actor used a variety of infostealers to collect session information and access Claude accounts belonging to an unknown number of users.
Forget the confusing branding and focus on your shrinking token bill