Anthropic tosses agents into the API billing pool
Limits Claude subscriptions to interactive use
Aggregated from vendor advisories, security research, and industry publications.
Limits Claude subscriptions to interactive use
OpenAI says two employees' devices were breached in the recent TanStack supply chain attack that impacted hundreds of npm and PyPI packages, causing the company to rotate code-sign…
On the first day of Pwn2Own Berlin 2026, security researchers collected $523,000 in cash awards after exploiting 24 unique zero-days. [...]

Data center outages are becoming less frequent overall, but resiliency gains are slowing as data center operators face mounting pressure from AI workloads, aging power infrastructu…
Why is IPv6 so much more complicated than IPv4? Could a newer version such as IPv8 be the solution? Guest Brian Carpenter joins our hosts to explain that many of IPv6’s complicatio…

Cisco has released updates to address a maximum-severity authentication bypass flaw in Catalyst SD-WAN Controller that it said has been exploited in limited attacks. The vulnerabil…
Today’s topic is Network Access Control (NAC) for a wired network. To help walk us through it all is Jennifer “JJ” Jabbusch, a network security architect, public speaker, book auth…
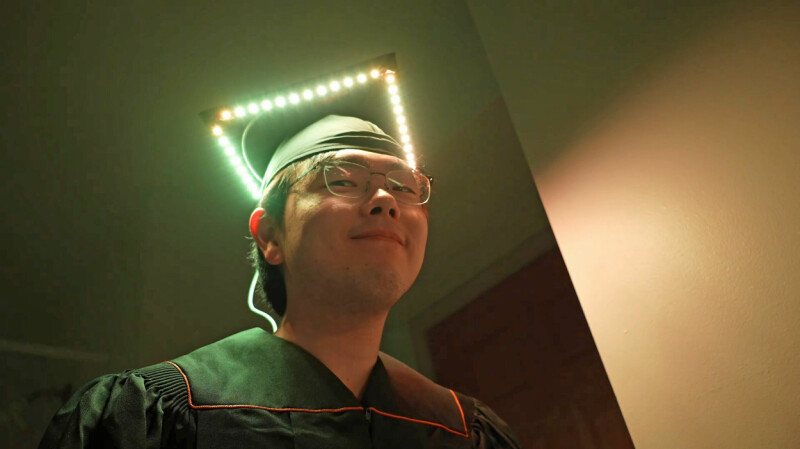
Eric Park tells us he doesn't plan to wear his modified cap to commencement, but his code's available for anyone with no such qualms and an upcoming ceremony

Cybersecurity researchers are sounding the alarm about what has been described as "malicious activity" in newly published versions of node-ipc. According to Socket and StepSecurity…
Multiple vulnerabilities in Cisco Catalyst SD-WAN Manager, formerly SD-WAN vManage, could allow a remote attacker to gain access to sensitive information, elevate privileges, or ga…

Everything is still on fire. This week feels dumb in the worst way — bad links, weak checks, fake help desks, shady forum posts, and people turning supply chain attacks into some c…
This is a current list of where and when I am scheduled to speak: I’m giving a virtual talk on “The Security of Trust in the Age of AI,” hosted by the Financial Women’s Associatio…
May 2026: This security advisory provides the details and fix information for a vulnerability that was discovered and fixed after the Cisco Catalyst SD-WAN Controller Authenticatio…
An 18-year-old flaw in the NGINX open-source web server, discovered using an autonomous scanning system, can be exploited for denial of service and, under certain conditions, remot…
Germany's Sovereign Tech Fund backs the desktop project while public sector interest in homegrown alternatives grows
Cargo theft now starts with phishing emails and stolen credentials, not hijackings, to reroute and steal freight from supply chains. NMFTA outlines how cyber-enabled cargo crime is…
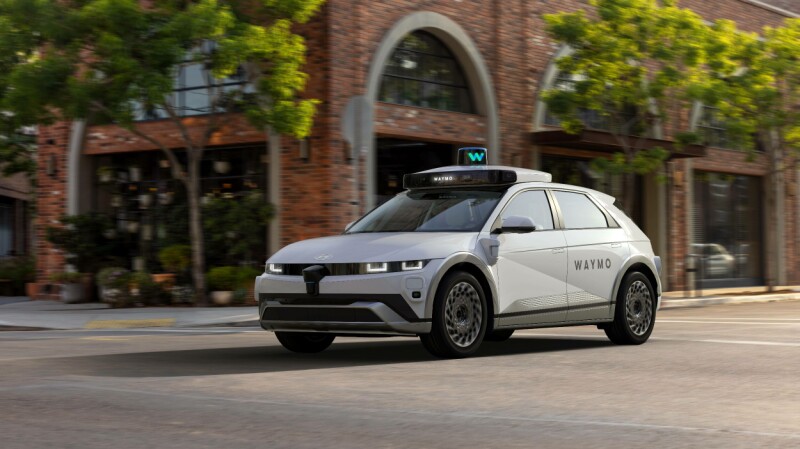
Nothing like a partly submerged self-driving car to dampen public trust in autonomous vehicles

Cisco Systems delivered a blowout Q3 FY2026 performance that surpassed even the most optimistic expectations, posting record revenue of $15.8 billion, up 12% year-over-year, with p…
Brit regulator has 'heard' customers can't always 'effectively combine software from Microsoft with that of other providers'
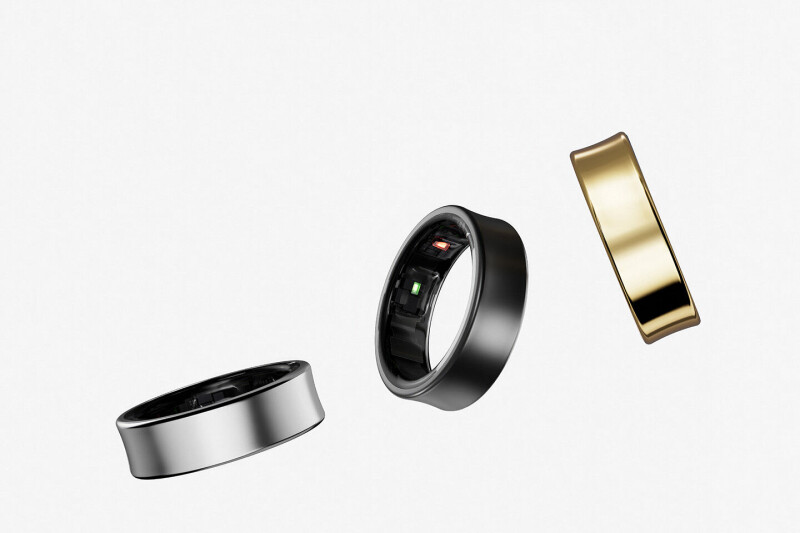
And Counterpoint sees fad spreading from pricey handsets to smart rings and earbuds too... whether you asked for it or not

The Belarus-aligned threat group known as Ghostwriter has been attributed to a fresh set of attacks targeting governmental organizations in Ukraine. Active since at least 2016, Gho…
For AI data centers, where the stakes are the highest and performance constraints are the tightest, security and performance are no longer a zero-sum game. The post Enhancing Data …
The vulnerability, tracked as CVE-2026-46300, is similar to the recently disclosed exploits named Dirty Frag and Copy Fail. The post New Linux Kernel Vulnerability Fragnesia Allows…
AI to the rescue as 11-year search for password turns up in old PC files
Version 1.3.14 of JavaScript toolkit released as last Zig version; a million lines of Rust code merged in gargantuan commit
Independent benchmarking finds Mythos highly effective for source code audits, reverse engineering, and native-code analysis, though its exploit validation and reasoning capabiliti…
In a role reversal, investment dollars in security startups exceeded the value of mergers and acquisitions in 1Q26 by more than $1 billion, a rare occurrence.
The acquisition enables Akamai to expand its Zero Trust portfolio to add protection directly into the browser. The post Akamai to Acquire AI and Browser Security Firm LayerX for $2…
AI and the bit barns that power it have developed a serious PR problem
Initial access broker KongTuke has moved to Microsoft Teams for social engineering attacks, taking as little as five minutes to gain persistent access to corporate networks. [...]