
Utah tells porn sites to take the P out of VPNs, and it's their fault that they can't
Governments can't touch VPNs technically or commercially. The mess they'll make if they try will be off the scale
Aggregated from vendor advisories, security research, and industry publications.
Governments can't touch VPNs technically or commercially. The mess they'll make if they try will be off the scale
Haters are gonna hate the fact Bobby Prince's demonic dirges rank with Taylor Swift's 1989
The flaw leads to denial-of-service on default configurations and to remote code execution if ASLR is disabled. The post Exploitation of Critical NGINX Vulnerability Begins appeare…
A recently patched local privilege escalation vulnerability in the Linux kernel's rxgk module now has a proof-of-concept exploit that allows attackers to gain root access on some L…

A new analysis of the Lua-based fast16 malware has confirmed that it was a cyber sabotage tool designed to tamper with nuclear weapons testing simulations. According to Broadcom-ow…
Letting a 21-year-old write critical code without supervision is not smart
No customer info stolen, no impact to operations, and no blackmail payment
The Pwn2Own Berlin 2026 hacking contest has concluded, with security researchers collecting $1,298,250 in rewards after exploiting 47 zero-day flaws. [...]

Chaotic Eclipse, the security researcher behind the recently disclosed Windows flaws, YellowKey and GreenPlasma, has released a proof-of-concept (PoC) for a Windows privilege escal…
Participants demonstrated exploits for Windows, Linux, VMware, Nvidia, and AI products. The post Hackers Earn $1.3 Million at Pwn2Own Berlin 2026 appeared first on SecurityWeek.
PLUS: China-linked cyber-attack on central Asian oil sector; Bottom falls out of Indian smartphone sales; And more!
South Korea's local elections next month will be a test bed for how effective regulations might be to stymie the flow of deepfakes.
Multiple researchers using the same tools to find the same bugs are creating ‘unnecessary pain and pointless work’
Stuck with an AI bill for tens of thousands of dollars? You're not alone by a long shot
A cybersecurity researcher has released a proof-of-concept exploit for a Windows privilege escalation zero-day dubbed "MiniPlasma" that lets attackers gain SYSTEM privileges on ful…
Ride your bots further by putting them in a harness
The Tycoon2FA phishing kit now supports device-code phishing attacks and abuses Trustifi click-tracking URLs to hijack Microsoft 365 accounts. [...]
You're not the only one annoyed by the hype

A newly disclosed security flaw impacting NGINX Plus and NGINX Open has come under active exploitation in the wild, days after its public disclosure, according to VulnCheck. The vu…
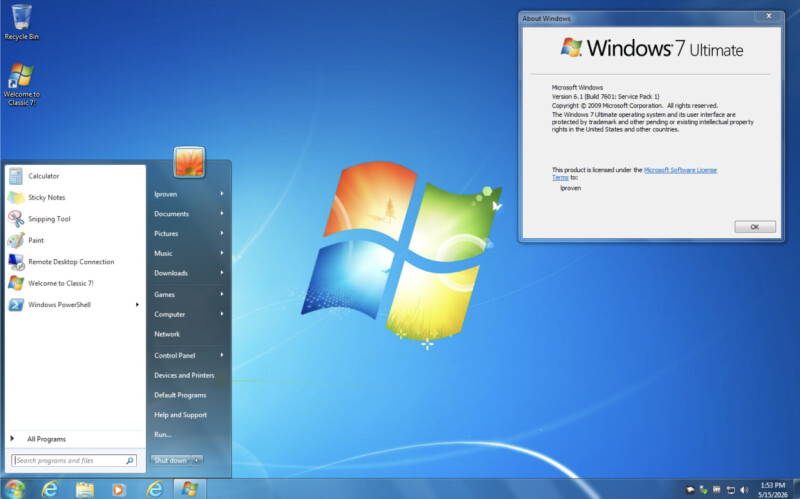
Uncanny rebuild resurrects the 2009 desktop, complete with support, updates, and licensing questions
Are you ready to RAAC?

Grafana has disclosed that an "unauthorized party" obtained a token that granted them the ability to access the company's GitHub environment and download its codebase. "Our inv…
A security researcher claims Microsoft quietly fixed an Azure Backup for AKS vulnerability after rejecting his report, and without issuing a CVE. Microsoft disputes the claim, tell…
The boom is piling up technical debt, warns Lightrun's Moshe Sambol

A critical security vulnerability impacting the Funnel Builder plugin for WordPress has come under active exploitation in the wild to inject malicious JavaScript code into …
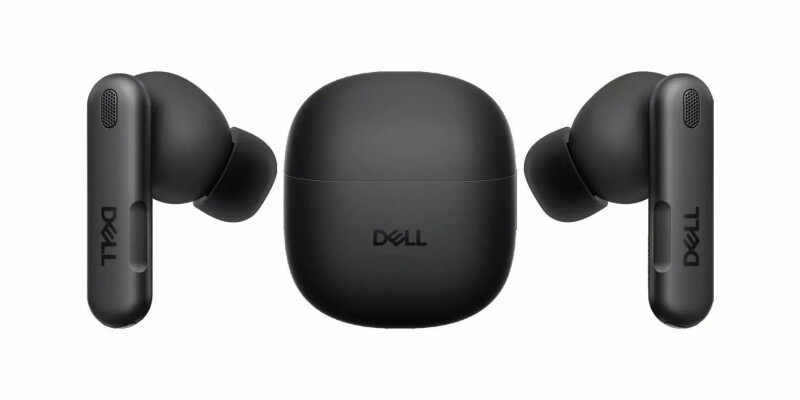
The Register tests Dell’s first attempt at outplaying Apple’s AirPods
The Russian hacker group Secret Blizzard has developed its long-running Kazuar backdoor into a modular peer-to-peer (P2P) botnet designed for long-term persistence, stealth, and da…
Intel ME and AMD PSP: The silicon layer nobody certifies
Introduced in 2008, the critical-severity security defect was patched this week in NGINX Plus and NGINX open source. The post PoC Code Published for Critical NGINX Vulnerability ap…
Patients are using chatbots for medical advice, while the NHS is still debating where AI belongs