Datacenter builds could be shielded from judicial review in UK planning reforms
British government wants to ensure no hold-ups for critical energy and infrastructure projects
Aggregated from vendor advisories, security research, and industry publications.
British government wants to ensure no hold-ups for critical energy and infrastructure projects
Old, busted, insecure authentication to be replaced with something shinier and safer
Big Blue spinout eyes up to $500M in savings and agentic AI while insiders grumble it's still 'IBM without the hardware'
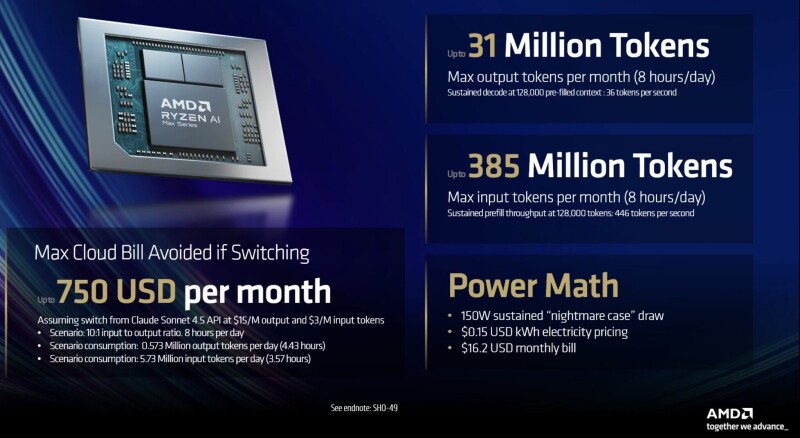
Assuming you’re vibe coding for 8 hours a day, that is

New Industry Data Just Released Suggests Not. On May 19th, 2026, Orchid Security released the results of our Identity Gap: Snapshot 2026. Among the findings, "identity dark matter…
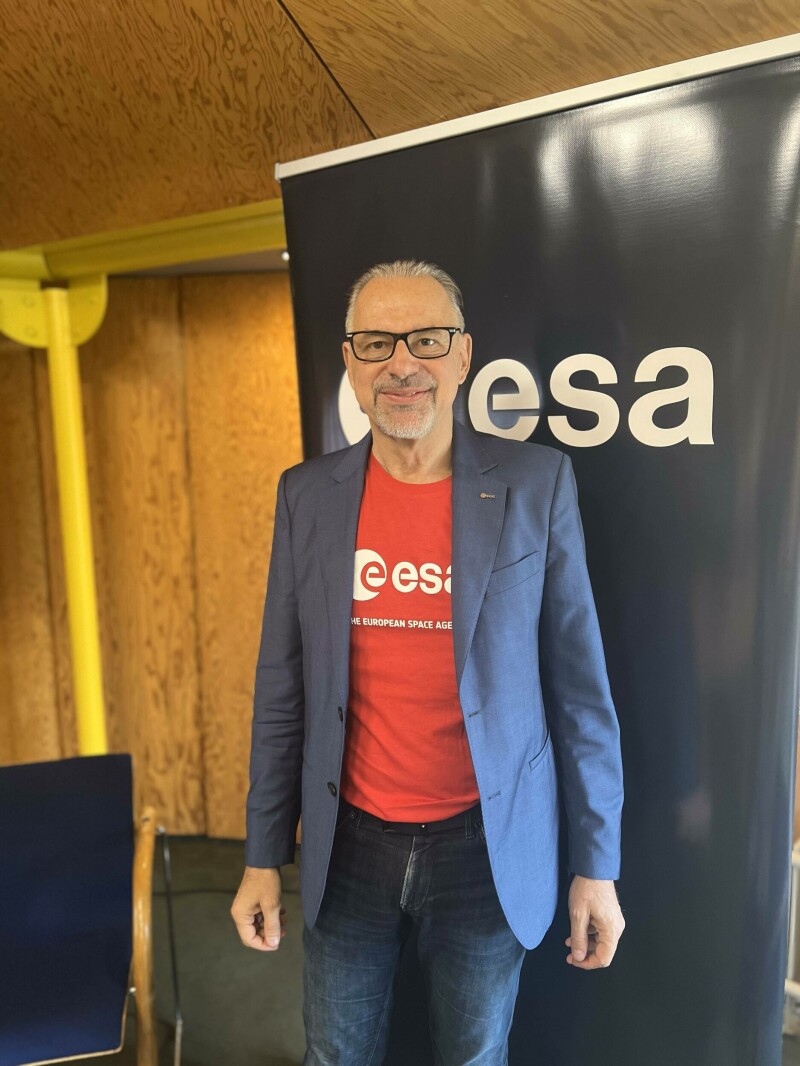
Are we pilots or are we passengers? Aschbacher asks
A compromised maintainer account was used to publish malicious package versions across the @antv namespace. The post Over 320 NPM Packages Hit by Fresh Mini Shai-Hulud Supply Chain…
As enterprises rush AI projects into production, security teams are increasingly being forced into reactive mode. The post Caught Off Guard: Securing AI After It Hits Production ap…
PinTheft, a recently patched Linux privilege escalation vulnerability, now has a publicly available proof-of-concept (PoC) exploit that allows local attackers to gain root privileg…

AI-generated lookalike domains are now embedded inside the third-party scripts running on your web properties. Here's why your current stack can't see them, and what detection actu…
Initial assessment says customer data spared while users wonder what else may have slipped out
SecurityWeek spoke with several ICS security experts and companies about their most memorable experiences in the field. The post Real-World ICS Security Tales From the Trenches app…
Don't miss this virtual event as we explore how to cut through alert fatigue, leverage AI and unified platforms to accelerate investigations, and apply actionable threat intelligen…
Government Commercial Agency wants DIPS 2 to reach beyond MoD buyers and the usual big-name suppliers
The TeamPCP hacking group accessed the repositories after a GitHub employee installed a poisoned VS Code extension. The post GitHub Confirms Hack Impacting 3,800 Internal Repositor…
AWS, Percona, Supabase, pgEdge, and Tiger Data rally round pgBackRest with funding pledge
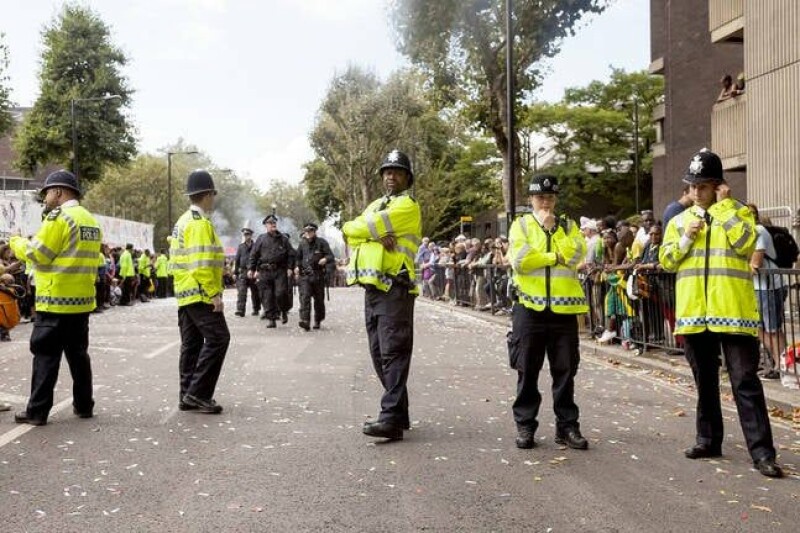
A Freedom of Information Act request shows the extent of the surveillance

Microsoft on Tuesday released a mitigation for a BitLocker bypass vulnerability named YellowKey following its public disclosure last week. The zero-day flaw, now tracked as CVE-20…
Through its "All in AI, AI for All" vision, ZTE surpasses climate targets, bridges the global digital divide, and strengthens governance resilience
GitHub has confirmed that roughly 3,800 internal repositories were breached after one of its employees installed a malicious VS Code extension. [...]
Microsoft has shared mitigations for YellowKey, a recently disclosed Windows BitLocker zero-day vulnerability that grants access to protected drives. [...]
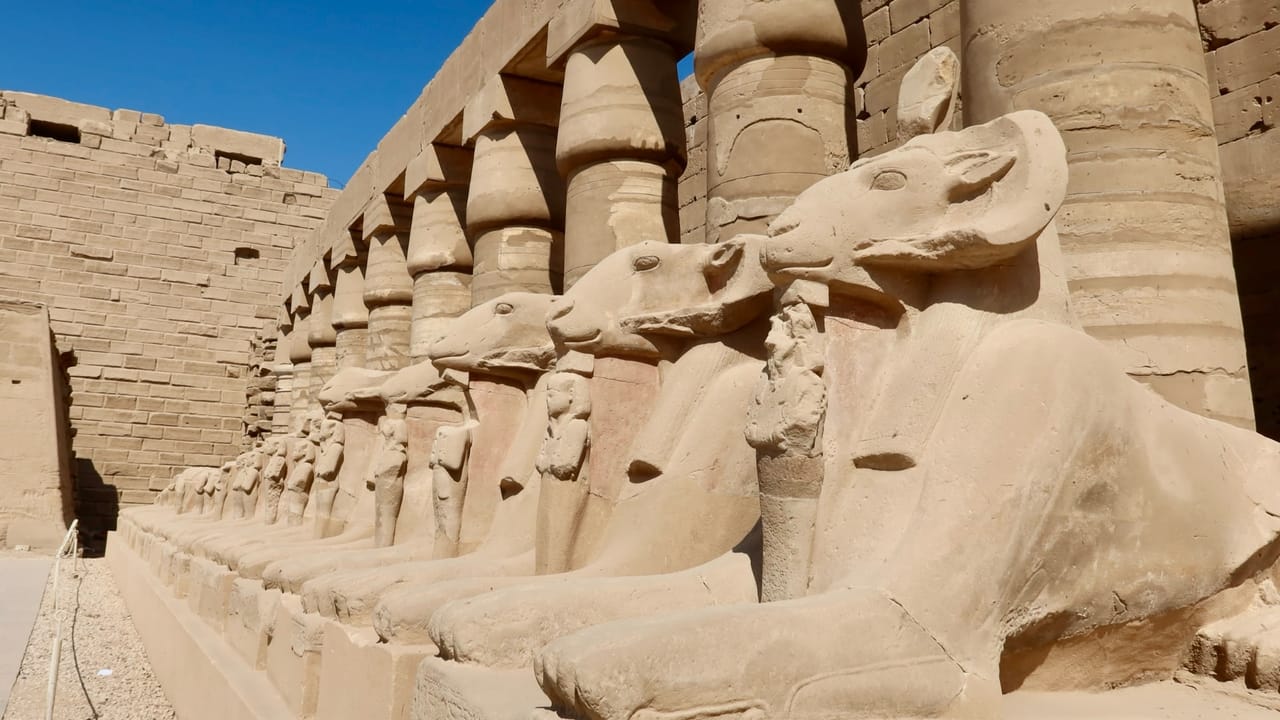
While the numbers are modest, the crackdown on cybercrime involved 13 countries in the MENA region, the largest law enforcement collaboration to date.
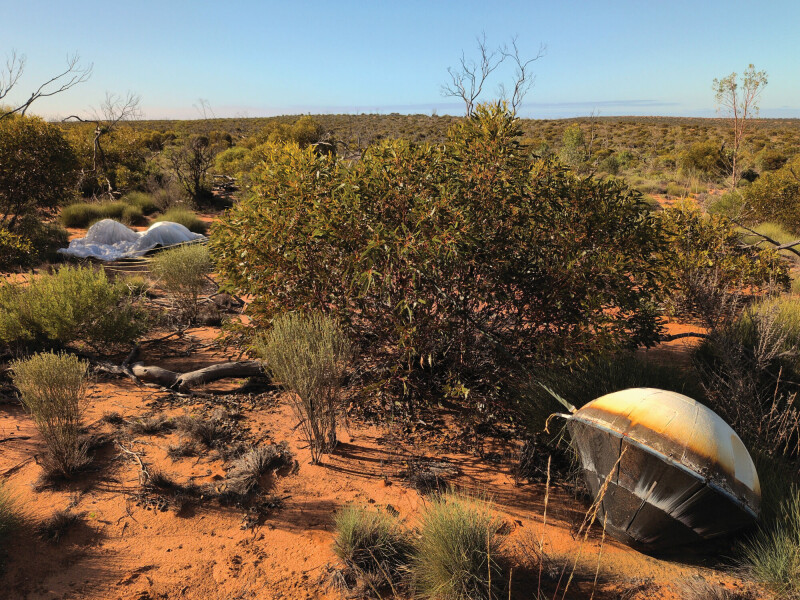
Varda hails success of autonomous touchdown tech and celebrates heat data haul

Grafana Labs, on May 19, 2026, said an investigation into its recent breach found no evidence of customer production systems or operations being compromised. It said the scope of …
GitHub is investigating a breach of its internal repositories after the TeamPCP hacker group claimed to have accessed approximately 4,000 repositories containing private code. [...…
This is the service we get when we spend $10m plus? asks automated code deployment outfit

GitHub on Tuesday said it's investigating unauthorized access to its internal repositories after the notorious threat actor known as TeamPCP listed the platform's source code and i…
Five ways CISOs can prepare for consuming AI bills of materials and influence the direction of how they're generated.
Minister demands AI becomes ‘basic expectation for all public entities’
Verizon’s 2026 DBIR finds vulnerability exploitation has overtaken credential abuse as the leading breach vector, as AI accelerates attacks, patching delays worsen, and ransomware …