HPE declares Juniper deal a 'home run' as AI and networking fuel record quarter
Networking orders surged, AI demand showed little sign of slowing, and HPE used the occasion to take a victory lap over its $14 billion Juniper bet
Aggregated from vendor advisories, security research, and industry publications.
Networking orders surged, AI demand showed little sign of slowing, and HPE used the occasion to take a victory lap over its $14 billion Juniper bet

A Palo Alto Networks vulnerability that allows attackers to establish unauthorized VPN access into corporate networks is being actively exploited in the wild, weeks after the compa…
Google has released the June 2026 Android security patches to address 124 vulnerabilities, including one zero-day flaw exploited in targeted attacks. [...]
As part of their 20th Anniversary celebration, Dark Reading asked five cybersecurity industry leaders who wrote blogs or columns for them over the years to select their favorite pi…
An anonymous security researcher called “Nightmare Eclipse” has been publishing a series of significant security exploits against Microsoft Windows—including one that breaks BitLoc…
Exploiting a confused deputy weakness, the hackers simply asked the chatbot to link the account to a new email address. The post Meta AI Hands Over High-Profile Instagram Accounts …
If you’re going to impersonate an officer, perhaps choose a more sophisticated way to nick cash than asking for gift cards…

Most organizations now recognize that endpoint protection alone is no longer sufficient. That's why adoption of endpoint detection and response (EDR) has accelerated rapidly in re…
Britain's former US ambassador founded lobbyist that represented spy-tech firm, saw it win big roles in UK defense, health tech
Hackers published 96 malicious package versions, injected with a credential-stealing worm similar to Mini Shai-Hulud. The post Supply Chain Attack Hits 32 Red Hat NPM Packages appe…
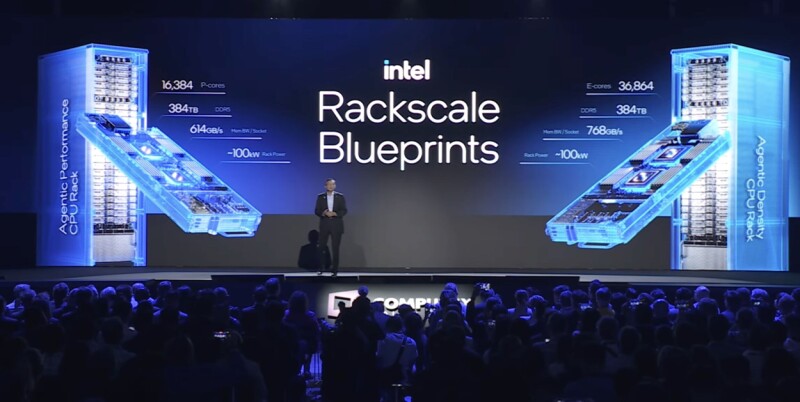
Meanwhile, Intel and SambaNova's disaggregated inference blueprint lands its first customer

Cybersecurity researchers have disclosed details of a spear-phishing campaign likely undertaken by the Pakistan-aligned SideCopy group targeting Afghanistan's Ministry of Finance w…
Nice technology, shame about the price and the indoor blackouts
Dashlane’s security systems automatically locked accounts to protect them against the hacking attempts. The post Dashlane Brute-Force Attack Leads to Limited Encrypted Vault Downlo…
Oracle’s monthly Critical Security Patch Update (CSPU) rollouts are meant to deliver critical fixes faster. The post Oracle’s First Monthly Patches Resolve 77 Vulnerabilities appea…

Password manager Dashlane has disclosed that "fewer than" 20 users on the personal subscription plan had their encrypted vaults downloaded following a brute-force attack launched b…

Microsoft continues to face scrutiny over its alleged antitrust practices, with new details coming to light about what, exactly, the federal government is investigating about the t…
'16% of my monthly Pro+ allowance. Gone. For basically nothing'
A threat actor tracked as DriveSurge has been operating large-scale malware distribution campaigns using ClickFix and FakeUpdates techniques on compromised sites. [...]
TeamPCP? Or copycat malware dev?
More than 30 npm packages under Red Hat's '@redhat-cloud-services' namespace were compromised in a supply-chain attack that distributed a new variant of the Shai-Hulud credential-s…
The Spanish National Police has arrested an individual for leaking sensitive information related to members of various key state organizations, including the National Cybersecurity…
The European security agency's entry to Project Glasswing is the result of "strong bilateral cooperation" between the European Commission and Anthropic.
Hacking voting machines is so 2017. Phishing, impersonation pose the real election risks

As the DRAM shortage continues with no end in sight, China-based ChangXing Memory Technologies (CXMT) is taking advantage of an opportunity to grow its base. Until now, CXMT has…
After a disgruntled security researcher published several zero-day exploits in recent weeks, Microsoft seemingly indicated criminal charges were in order.

Broadcom and Samsung Electronics are collaborating on a new, broadband-optimized reference platform for the global fixed wireless access (FWA) market, integrating Broadcom’s Wi-Fi …
The security defect (CVE-2026-8732) allows unauthenticated attackers to create administrative accounts on the affected installations. The post WP Maps Pro Vulnerability Exploited t…
Multiple Dashlane users have been locked out of their accounts following brute-force attacks that attempted logins from distant locations and unknown devices. [...]
First it tops OpenAI's valuation, then it beats Altman to the IPO punch