CISA slaps its tightest three-day patching deadline on perfect-10 Oracle flaw
Disclosed in January and honeypots buzzed soon after, CISA says it’s finally time for the USG to plug the gap
Aggregated from vendor advisories, security research, and industry publications.
Disclosed in January and honeypots buzzed soon after, CISA says it’s finally time for the USG to plug the gap
Andy Ellis has a roundup of the security vendors at Black Hat this year. Key Takeaways: We have entered into an AI world. While nearly half of booths didn’t directly mention AI or…
Law enforcement agencies from 22 countries helped identify 263 suspects and arrested 58 individuals linked to cybercrime networks coordinated by African crime groups. [...]
Silent patches can become exploit intelligence for attackers while leaving defenders without the context needed to prioritize risk. The post Silent Patches Don’t Stop Attackers – T…
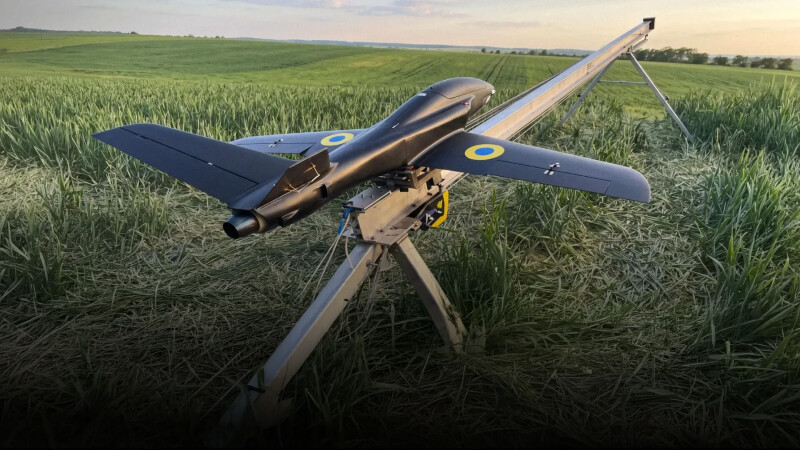
Fast and lightweight unmanned aircraft is designed for easy deployment and fits in a pickup truck
Sponsored search results lead developers straight into a ClickFix malware trap
Building a business case for moving enterprise workloads to the cloud or even switching cloud providers can itself be a lengthy exercise, requiring enterprises to first understand …

Bad actors are attempting to exploit two severe unauthenticated authentication bypasses in the Xecurify miniOrange SAML 2.0 Single Sign On plugin that make it possible for an attac…
Taxman wants to drag creaky NPS into agile era
AI infrastructure, including advanced semiconductors mostly made in Taiwan, has become a key point of competition between the U.S. and China. The post Taiwan Charges 9 Over Illegal…
SPONSORED EXPLAINER: Why you should take a long-term approach to rethinking your virtualization portfolio
The vulnerability is tracked as CVE-2026-21962 and it has been widely exploited by threat actors against WebLogic servers. The post CISA Warns of Exploited Oracle WebLogic Vulnerab…
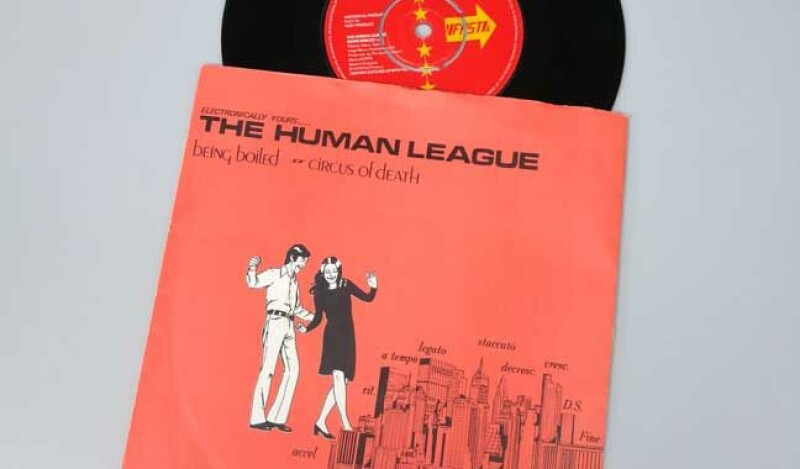
This is basically a riff on ‘You wouldn’t steal a car’ and means only the human league can have a hit

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a maximum-severity security flaw impacting Oracle HTTP Server and Oracle WebLogic Server to its Kno…
And fly ‘significant scale’ in 2028 – a claim that isn’t entirely bonkers, but needs a solid grain of salt
The semiconductor industry is becoming a trillion-dollar growth engine as AI gobbles up more and more resources. Gartner has slightly increased its forecast for worldwide semico…
Cunning plan to expand the amount of software that runs on mainframes is also an admission ISVs are focusing their energies elsewhere
Privacy? Not if you use hosted AI services
On top of July’s 30% price hikes across almost all of its product lines, Nvidia is reportedly preparing to raise prices of servers, including those powered by Vera Rubin and Grace …
CISA issued a three-day deadline for agencies to patch a Zimbra security vulnerability, CVE-2026-73570, which allows full takeover of a user's communications.
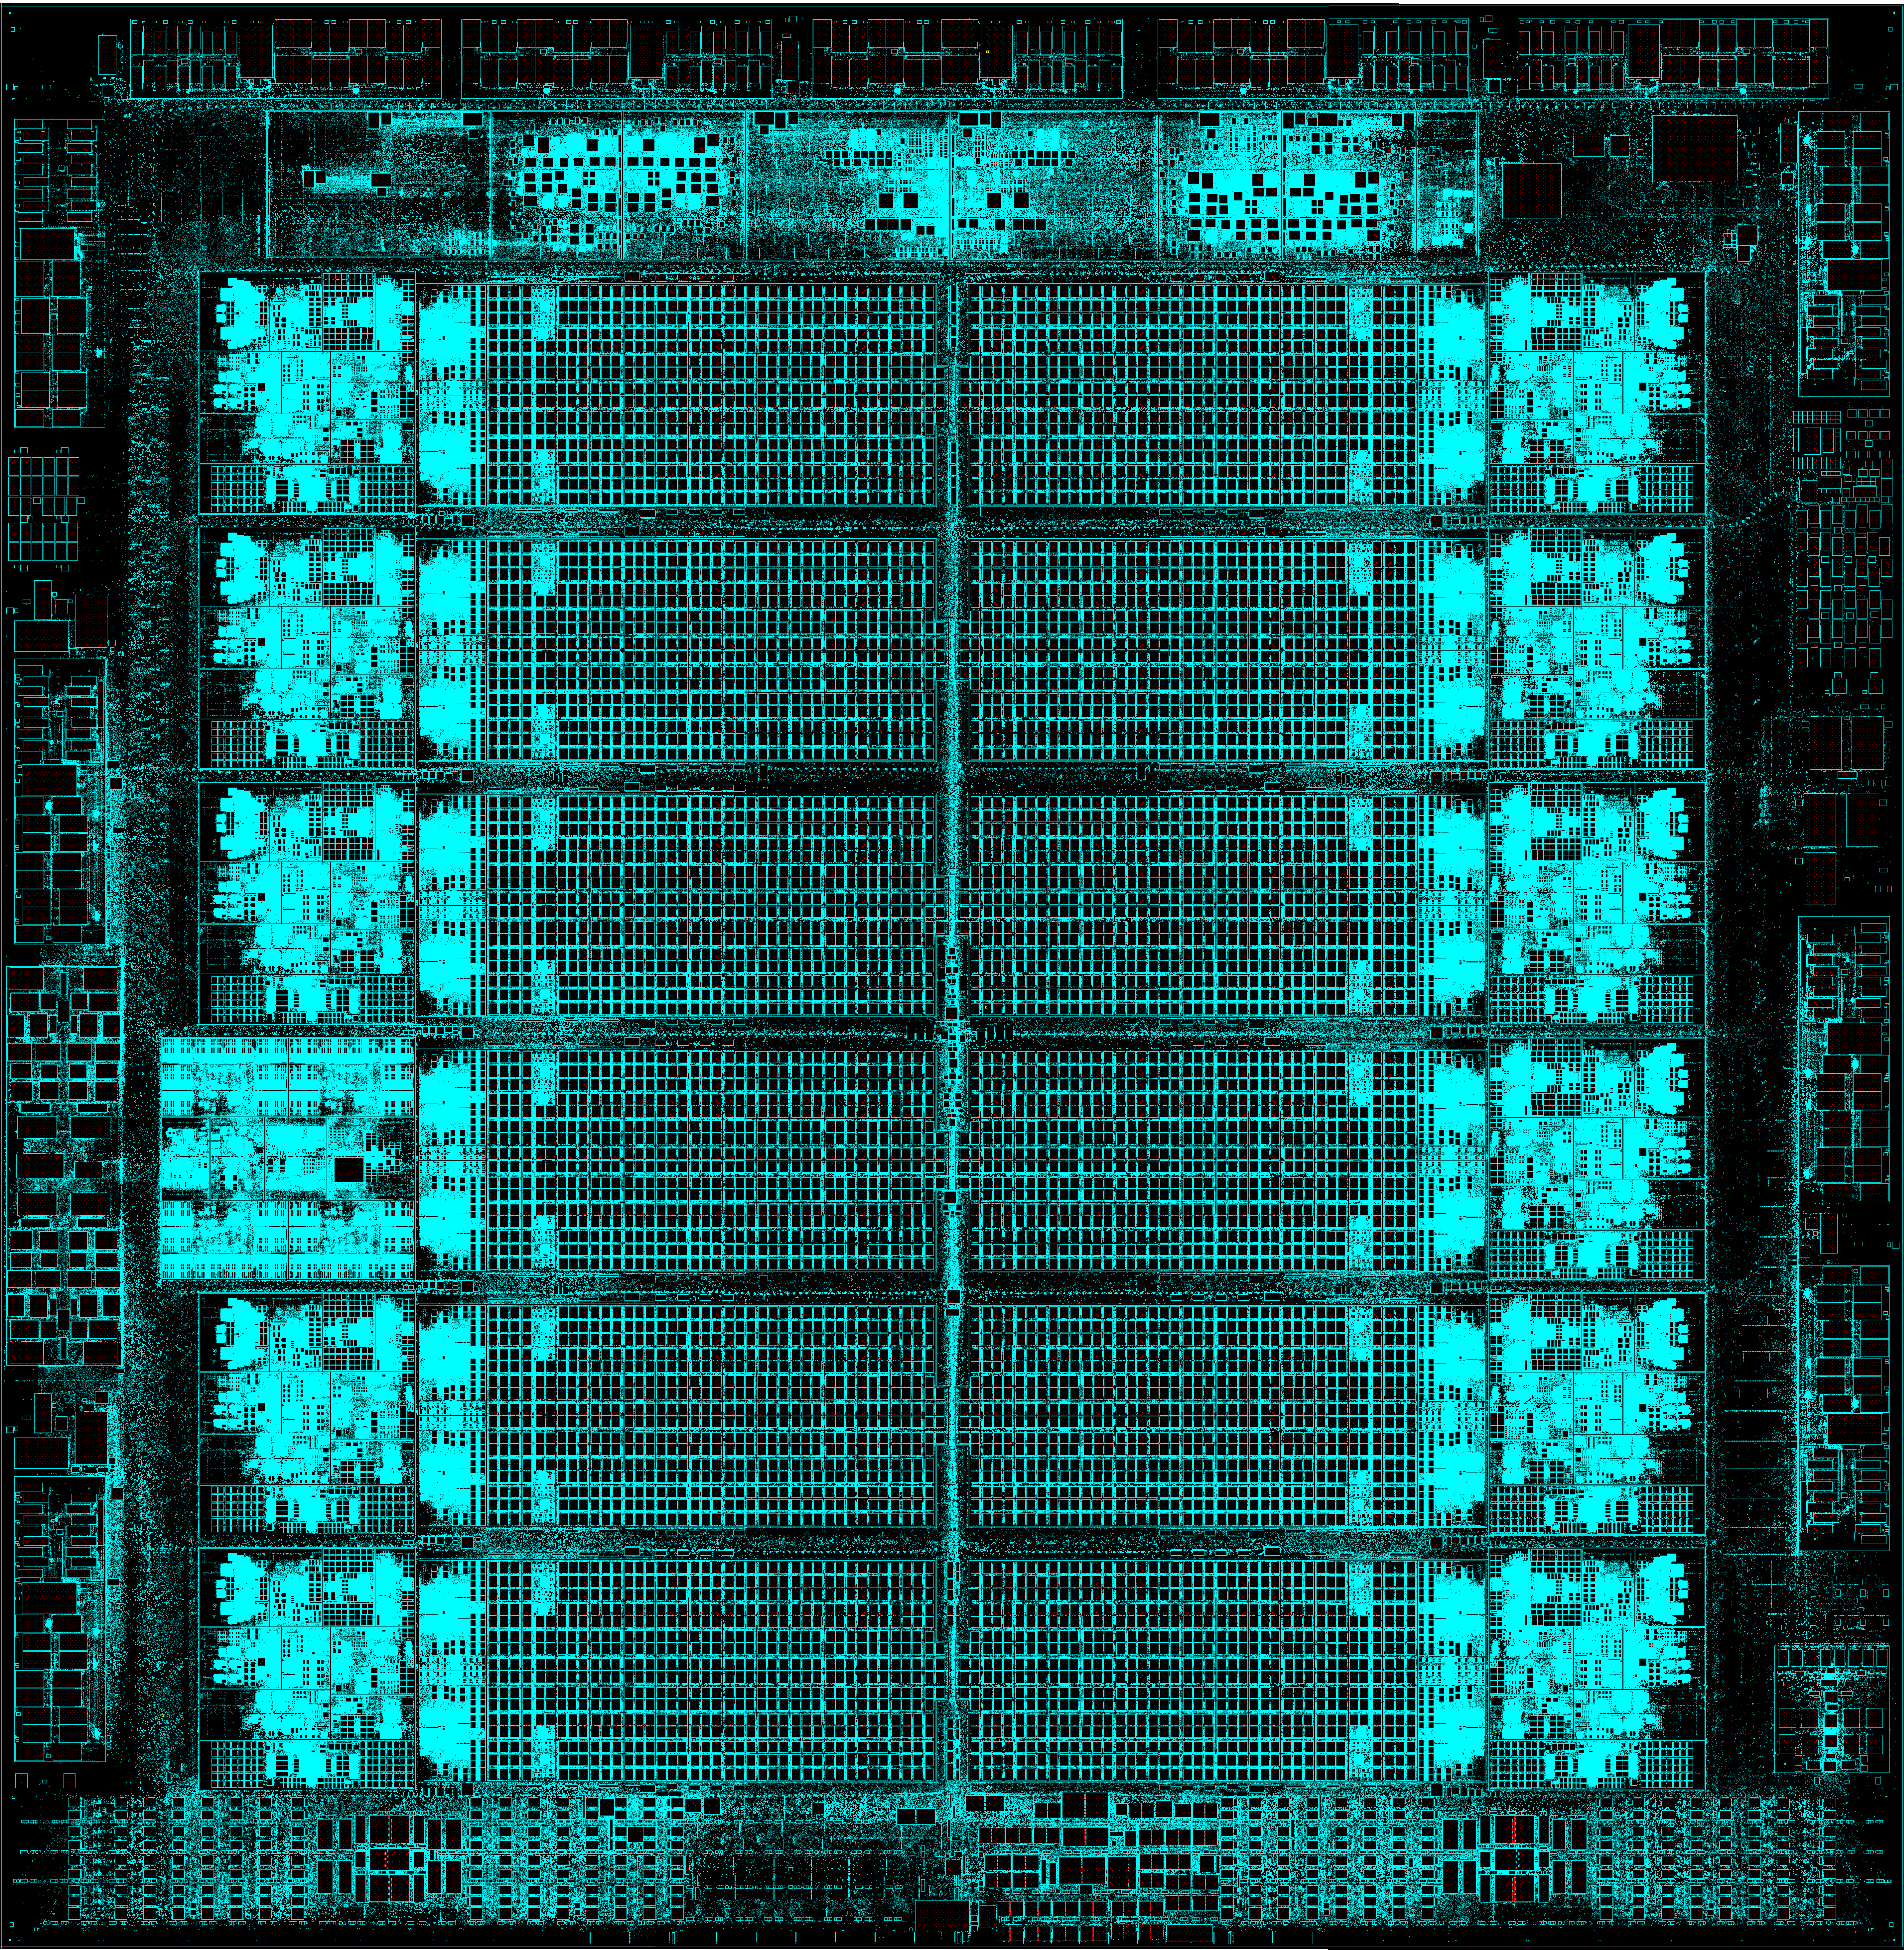
IBM announced its first dual-architecture mainframe processor that’s designed to allow enterprises to run Arm-native Linux environments alongside z/OS and existing Linux applicatio…
Its own command language, 23 instructions - signs point to 'well-resourced operation rather than an opportunistic one'
An unpatched vulnerability in Calix GS7 XGS (GS5239XG) residential routers used by multiple U.S. broadband providers allows remote, unauthenticated attackers to create port-forward…
Glassbox dev admits he had some help from Claude to build locally running tool
ClickFix-style threat campaigns are using a new trick to evade detection and deliver Amatera, an increasingly prevalent infostealer.
Darkbloom distributed inference network promises to put underutilized Apple kit to work
Hackers are attempting to exploit two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On plugin for WordPress that can be used to forge SAML r…
The U.S. Department of Justice announced a $400 million settlement with TikTok, ByteDance, and affiliated companies over allegations that they violated the Children's Online Privac…
The version that started to bring all Microsoft’s pieces together

Cybersecurity researchers have found that several websites are still actively distributing a malware family known as Weedhack to gamers by masquerading as Minecraft clients. McAfe…