Jensen's purchase of a new toy could reshape the entire AI industry
This week on The Kettle we weigh in on Nvidia's Hugging Face acquisition and why it could spell a new, more fragmented and siloed era of AI development
Aggregated from vendor advisories, security research, and industry publications.
This week on The Kettle we weigh in on Nvidia's Hugging Face acquisition and why it could spell a new, more fragmented and siloed era of AI development
Last week, he blamed himself for being ‘a grade A nincompoop’ who assumed a system upgrade couldn’t possibly go wrong
Article URL: https://gettogether.dev Comments URL: https://news.ycombinator.com/item?id=49592840 Points: 107 # Comments: 59
OpenAI is now rolling out ChatGPT Astra, its most powerful model to date, to those with a $20 Plus subscription, but there's no word on when free users will get access.. [...]
PLUS: Fujitsu not yet budgeting Horizon compensation; DeepSeek's vast Huawei GPU buy; Korea plans sovereign security model; and more
Threat actors have adopted the ASCII smuggling technique in phishing campaigns, using invisible Unicode characters to evade email security filters. [...]

Attackers are exploiting MikroTik routers with their Secure Shell (SSH) remote-access service, which is reachable from the internet, to gain full administrative control without aut…

Elastic Security Labs has documented four previously unreported programs associated with REVSTEALER, an emerging Windows information stealer, that remain on an infected machine aft…
Risk of an unprecedented negative adjustment prompts plan to let UTC drift by as much as an hour
DoD controls on mobile ad identifiers haven't stopped military location data turning up for sale

Attackers are exploiting a new unpatched vulnerability in Magento Open Source and Adobe Commerce that lets them run malicious code on an online store's server without logging in, D…

JetBrains is urging Cadence users to revoke and rotate all credentials following a security incident last month in which unidentified threat actors exploited a recently disclosed c…

Broadcom has released security updates for two security flaws impacting VMware Workstation and Fusion, including one critical bug that could result in arbitrary code execution unde…
A massive cybercriminal operation is leveraging thousands of compromised small-business websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain (BSC)…

Hardware wallet manufacturer Trezor on Friday disclosed that another 67,000 customers from the U.S. have been impacted in a breach at its shipping provider ShipMonk. The exposed i…
Tracked as CVE-2026-32475 (CVSS score of 9.8), the bug described as an arbitrary file upload issue in the function that handles form submissions. The post Elementor Pro WordPress P…
An unauthenticated attacker could exploit the security defects by sending crafted packets to the vulnerable service, achieving RCE with elevated privileges The post HPE Patches Cri…
OpenAI admits it did not disclose an incident where autonomous AI agents hijacked a German wiki, created 18,000 posts, shared answers, and bypassed restrictions, saying it treated …

A group of AI safety researchers says a fleet of autonomous agents that identified themselves as OpenAI systems left about 18,000 posts on a dormant 25-year-old German wiki between…

Threat actors are exploiting the newly disclosed PaperCut flaws to facilitate credential theft in attacks targeting the education sector in the U.S. and Europe. The Arctic Wolf Ad…
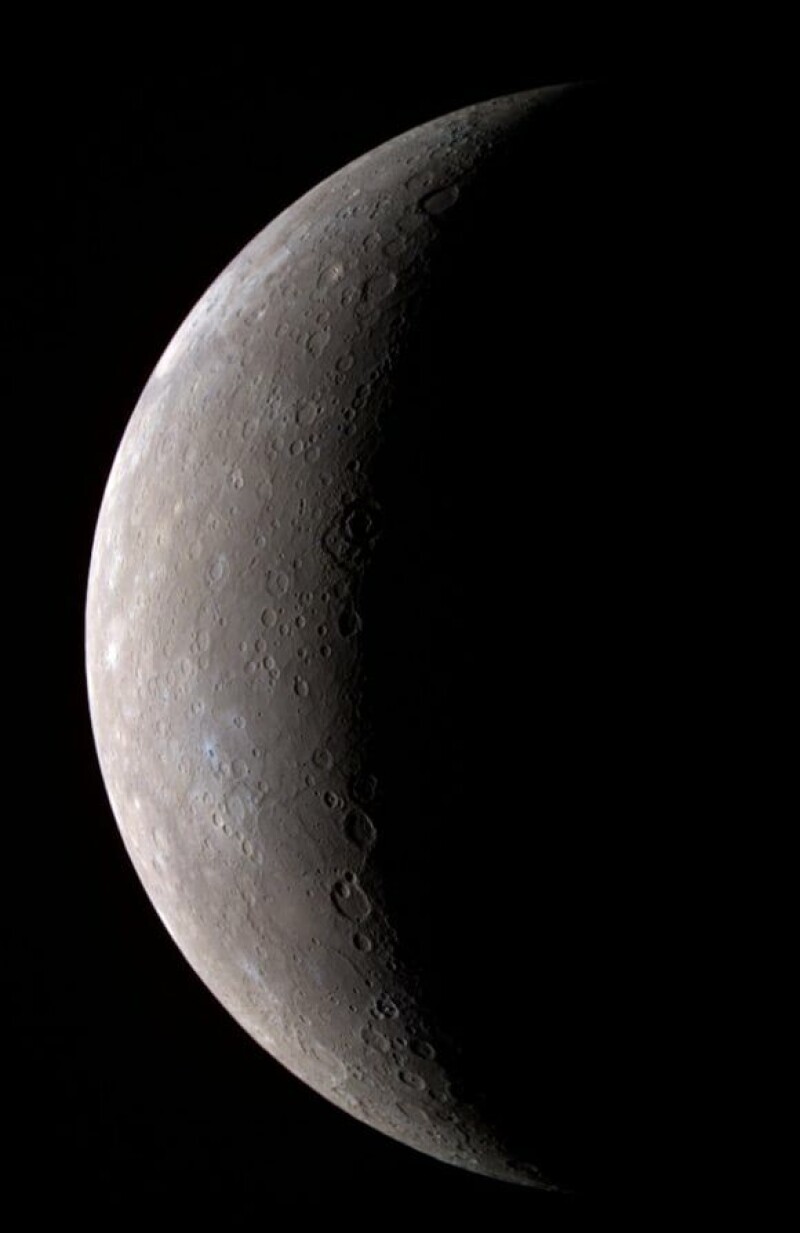
Eight years after launch, Mercury probe and its Mercury Transfer Module consciously uncouple as orbit approaches
Looks tasty. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation policy.
Now comes the harder sell: Convincing customers and merchants to trust AI with purchases
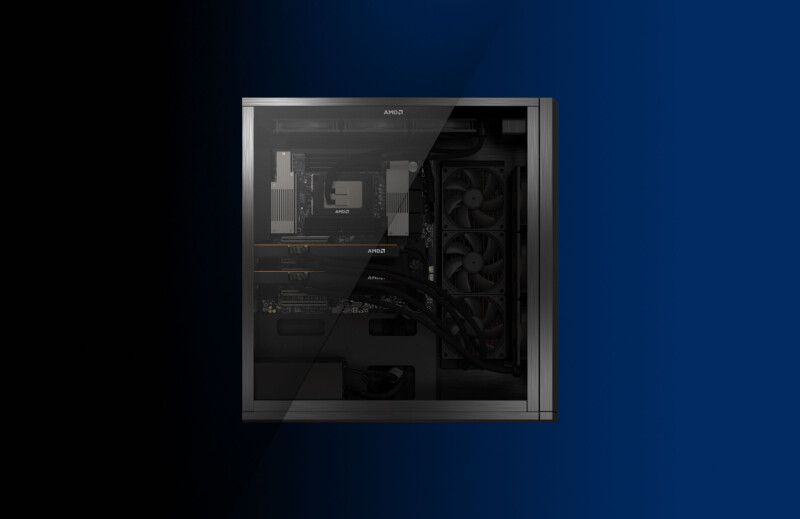
AI workstation promises to put up to 576 GB of HBM3e and 16 TB/s of memory bandwidth on your desk
Phishers find a new use for invisible Unicode tag characters
Article URL: https://rietta.com/blog/ruby-on-rails-cve-exploited-hours-after-patch/ Comments URL: https://news.ycombinator.com/item?id=49568828 Points: 117 # Comments: 38
Last year, 49,000 CVEs were published, more than 130 new vulnerabilities every day. So what actually happens with all of those CVEs in your network infrastructure? In this sponsore…
When engineers look to buy new technology they tend to focus on features and functionality, but there’s more to it than that. Sian Morgan joins Drew and Ethan to discuss the best p…
Multiple lawsuits have been filed against identity verification company IDScan after hackers allegedly breached the service and offered to sell more than 153 million driver's licen…
It won’t work: My suspicion was that GPT 5.6-Cyber would succeed, but the frequency and manner of its success removed all doubt. We have to reassess sandboxing quality for capable …