Mistral bags €3B to build Europe's sovereign AI champion
Samsung-led round values the French model maker at more than €21B
Aggregated from vendor advisories, security research, and industry publications.
Samsung-led round values the French model maker at more than €21B
The scammers purchased fleets of sports cars, flew on private jets, hired security guards and rented mansions in Miami and the Hamptons. The post Party’s Over for Crypto Scammers W…
Third-party applications connected to Google Workspace can retain access long after their original purpose is forgotten. This webinar examines how overly permissive integrations co…
Threat actors are increasingly switching from AI-powered coding assistants to multi-agent frameworks that automate every stage of an attack. [...]
Companies 'don't want their IP exposed, so they're willing to pay'
A Chinese-language group is compromising government and education sites to create a reverse-proxy network with gambling-themed sites.
Microsoft warned customers last week that they may experience application crashes on some Windows Server 2025 due to recent memory management changes. [...]

Researchers at the security firm Calif have built a worm that takes over a WeChat account via an incoming call and demonstrated it spreading among three test phones. The person be…

In the last six months, Chainguard doubled its output from 500 million to more than 1 billion container build manifests. We also surpassed 3,000 unique container images and 675,000…

A flaw in FreeIPA lets a client that has never logged in create a Kerberos identity of its own choosing in the directory and end up in the administrators group, Red Hat says. Free…
Proprietary platform keeps incumbent in place while NESO prepares a future competition
Dubbed MikroTrick, the bugs allow attackers to bypass authentication, overwrite configuration files, and take over devices. The post MikroTik Patches Critical Flaws Chained to Hack…
Hackers stole the information of students, teachers, staff, and parents/guardians from a self-hosted Metabase instance. The post Mathspace Data Breach Exposes Over 1 Million People…
Administrators are advised to check their deployments for newly created user accounts they don’t recognize. The post N-able Patches Critical Zero-Day in N-central appeared first on…
Dating app admits no liability over allegations that it shared sensitive user data, including HIV status, with third parties
Interesting research: “Stealing Reasoning Traces from Proprietary LLM APIs“: Abstract: Leading large language model providers now conceal their models’ step-by-step reasoning, or c…
Ministers declare war on an 'industry of dither and delay' as consultations, legal caution, and judicial reviews get the chop

Adobe on Monday released security patches to address a maximum-severity flaw impacting Adobe Commerce and Magento Open Source that has come under active exploitation in the wild. …
Cross-government plan combines civil ambitions with an increasingly military view of orbit

Cybersecurity researchers have disclosed details of a sprawling search engine optimization (SEO) poisoning campaign that paves the way for malware deployment and tech support scams…
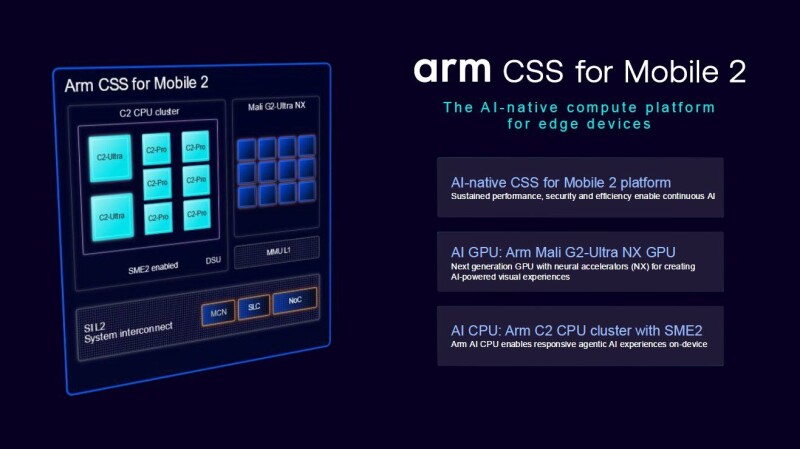
New CPU and GPU designs chase lower latency and richer games within a 1 W power budget
PARTNER CONTENT: Pairs block and adjacent file workloads with independent scaling of performance and capacity
Exclusive: An exposed Advance Passenger Information System (APIS) database held 220 million passenger and crew records containing names, passport numbers, dates of birth, nationali…

Online dating app Grindr has opted to pay £26 million ($35.1 million) to settle a lawsuit in the U.K. over allegations that it shared users' personal information, including their H…
CVSSv3 Score: 2.5 A NULL Pointer Dereference vulnerability [CWE-476] in FortiOS, FortiProxy and FortiPAM may allow an authenticated attacker to crash the httpsd daemon via cr…
CVSSv3 Score: 9.6 An Inclusion of Sensitive Information in Source Code vulnerability [CWE-540] in FortiMonitorOnSight web portal may allow a remote unauthenticated attacker t…
CVSSv3 Score: 5.9 A Use of Uninitialized Variable [CWE-457] vulnerability in Fortinet FortiAnalyzer SNMP daemon may allow a remote authenticated attacker with user permissio…
CVSSv3 Score: 4.7 An improper access control vulnerability [CWE-284] in FortiManager may allow an administrator to bypass the approval process for workflow sessions via craft…
CVSSv3 Score: 7.3 An improper certificate validation vulnerability [CWE-295] in FortiOS and FortiProxy Agentless ZTNA portal may allow a remote and unauthenticated attacker t…
CVSSv3 Score: 4.9 An Improper Access control vulnerability [CWE-284] in FortiSOAR may allow an authenticated attacker with zero permissions to subscribe to websocket streams …