SASE Converges Network & Security Into One Cloud Solution
Enterprise computing is moving to the edge. Keeping it secure requires tactics far beyond putting up firewalls. (Second in a three-part series.)
Aggregated from vendor advisories, security research, and industry publications.
Enterprise computing is moving to the edge. Keeping it secure requires tactics far beyond putting up firewalls. (Second in a three-part series.)
A new Android malware-as-a-service (MaaS) platform called RemControl is targeting users through malvertising campaigns that impersonate the TVTap IPTV application. [...]
A process parameter-poisoning technique evades EDR by injecting code into process initialization structures without using the Windows APIs that EDR tools typically watch out for.
Incoming email addresses automatically assigned to each user on the platform contain highly privileged access tokens that attackers can use.
Technology company F5 fixed a critical remote code execution vulnerability in its BIG-IP Access Policy Manager (APM) platform on Tuesday. The flaw impacts deployments configured as…
Jev-powered Slop Mop demonstrates another great use case for probabilistic, non-chatty AI model
Cybersecurity company Check Point has confirmed active exploitation of CVE-2026-85102, a pre-authentication remote code execution (RCE) vulnerability in the VPN certificate-handlin…
IonQ’s new single processor quantum error decoder minimizes the classical computing overhead in quantum error correction. The post IonQ Targets Quantum Error-Correction Bottleneck …
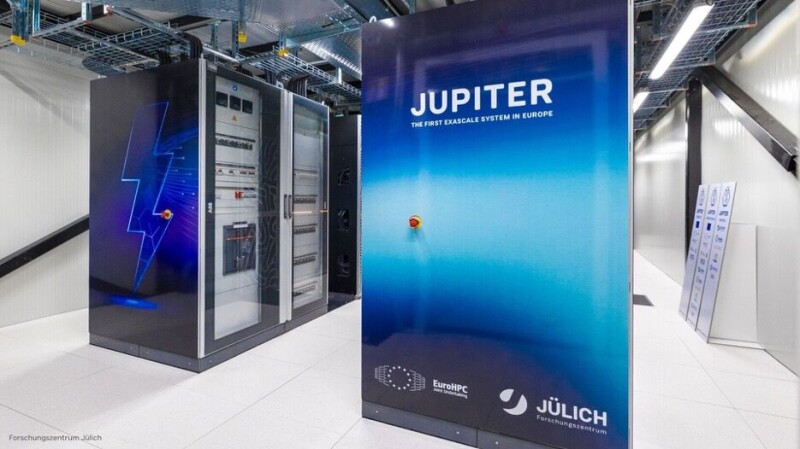
Bull, the system builder behind JUPITER, takes delivery of SiPearl's long-awaited Rhea1 CPUs
Threat actors have moved from probing WordPress sites vulnerable to CVE-2026-87902 to exploiting the flaw to write files to disk that execute shell commands when accessed. [...]
Good news: there's a patch. Bad news: both CISA and F5 warn that it's under active exploitation

Cybersecurity researchers have disclosed Go-based malware distributed via two Go Modules and two Terraform providers, marking the first time threat actors are using the centralized…
The idea that AI could break away and work toward its own agenda is looking increasingly plausible to researchers and experts. The post Worries About an AI Internet Takeover Gain N…
Discord users asked to prove they’re adults get less intrusive options

The private email address GitLab gives you for filing issues by email is a credential. Anyone who gets it can email a patch that GitLab commits in your name, to any branch you can …
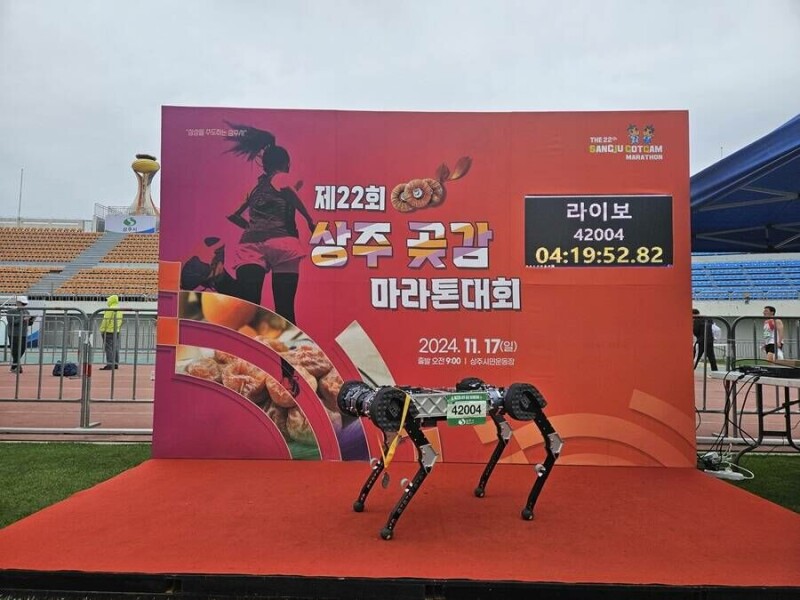
Two years later, creators explain how lightweight hardware and reinforcement learning helped it go the distance
A financially motivated threat actor is using open-source AI agent frameworks to attack hundreds of online retailers at scale, stealing more than 600,000 credit card records. [...]

Two MikroTik RouterOS SSH vulnerabilities chained together let attackers take full administrative control of Internet-exposed routers without a password, SSH key, or completed auth…
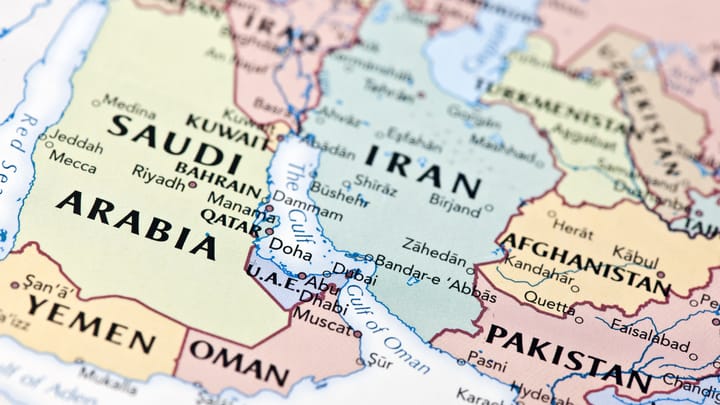
The United Arab Emirates and Kingdom of Saudi Arabia together absorbed 50% of all cyberattacks recorded across the Gulf region in the first half of 2026.
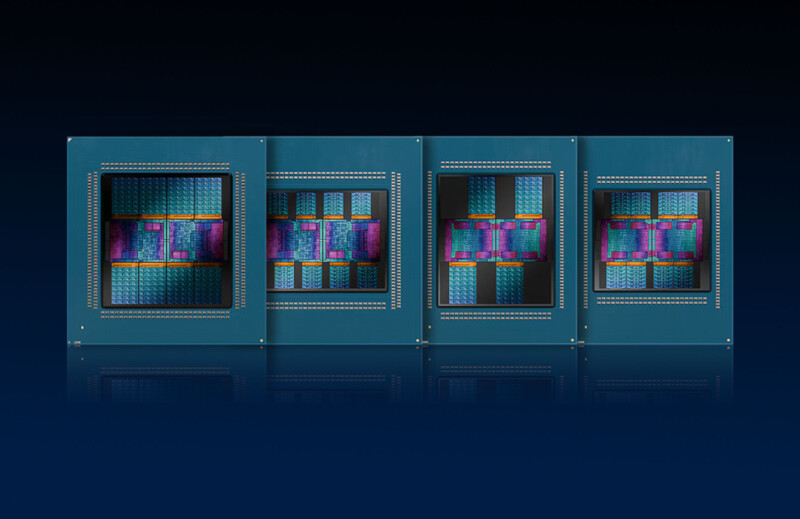
16 channels of DDR5, 5 GHz clock speeds, and support for CXL 3.1 memory god boxes? What's not to like?
Ned and Kyler talk with Jim Jones about data protection, backups, and security in the age of hybrid cloud and AI. They explore the operational challenges of integrating automated A…
Article URL: https://radicle.dev/2026/09/23/disclosure-of-vulnerability-in-network-protocol Comments URL: https://news.ycombinator.com/item?id=49817524 Points: 154 # Comments: 58
New dock and app launcher arrive while soaring memory prices revive scrutiny of a two-year-old firmware restriction
Customers got crime crew's calling card instead of access to journals
SPONSORED FEATURE: Why AI-driven operations need a data-rich view of the network
Network operations teams are being asked to hand real decisions to AI agents. Trusting an agent enough to let it act in production is a different problem than building one. Soft…
Threat actors are poisoning ChatGPT, Gemini, and Google AI Overview answers by seeding the Web with malicious links and data and then optimizing the content.
Attackers are increasingly targeting the management systems used to control enterprise infrastructure, with several critical vulnerabilities actively exploited before or shortly af…

A Windows malware called CLOSEDQUORUM is built to take orders from a vote of up to four AI models instead of an attacker's server, Cisco Talos said on September 22. The models can…
A Kubernetes user with limited permissions can potentially gain control of an entire Google Cloud organization by exploiting the authority granted to Google Kubernetes Config Conne…