Progress orders emergency ShareFile server shutdown over mystery security threat
Vendor insists there's no evidence of unauthorized access, but it's asking customers to take one of the most drastic precautions available
Aggregated from vendor advisories, security research, and industry publications.
Vendor insists there's no evidence of unauthorized access, but it's asking customers to take one of the most drastic precautions available
The flaw results in malicious code embedded in crafted emails being executed when the emails are opened. The post Zimbra Patches Critical Code Execution Vulnerability appeared firs…
The move targeted people and entities accused of links to an online spying network that the EU claims targeted governments and carried out sabotage operations against critical infr…
Nagware goes large on the mean streets of Derby
Cybersecurity agencies from the United States and eight other countries have issued a joint warning that Russian state hackers are targeting vulnerable and poorly configured router…
Solar boss reckons challenges are regulatory, not technological
Threat actors have been targeting Balbooa Forms and iCagenda Joomla extension flaws for remote code execution. The post Organizations Warned of Exploited Joomla Extension Vulnerabi…

Early in my consulting career, I assumed maintenance windows reduced risk. After all, the purpose of planned maintenance is to improve reliability, apply fixes and prevent future o…
Time for the Clone Wars remake
The company notified customers to manually shut down their servers while it is investigating a credible threat. The post Progress Prompts ShareFile Storage Zone Controller Shutdown…
The WorldLeaks extortion group claimed to have stolen 720 GB of data from the healthcare testing and laboratory services provider. The post Centers Laboratory Data Breach Affects 5…
PARTNER CONTENT: Firms crafting internal AI must choose a permanent residence for their tech, not just rent server space by the hour.
Lawsuit alleges job-swappers took secrets with them, helped by coaching on how to avoid scrutiny

An attacker running a live Microsoft 365 phishing operation left a Python web server listening on a public port with directory listing switched on. The command that did it: python3…
IT department was not pleased, but was also easily fooled

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two maximum-severity security flaws impacting iCagenda and Balbooa extensions for Joomla to its Known Exp…
Pulls AI-powered image tweaker after allowing free-for-all
PLUS: Canadian/Bhutanese datacenter for India; China re-uses a rocket; Australia signals AI intervention; And more!
OpenAI is temporarily relaxing GPT-5.6 Sol usage after demand for the company's most powerful model surged over the past 48 hours. [...]
Anthropic has just extended access to Claude Fable 5 for paid subscribers until July 19, giving you another week to keep using the most powerful model. [...]
A new version of the RedHook Android malware abuses the Android Wireless Debugging (Wireless ADB) mechanism in a novel way to gain shell-level privileges without requiring a comput…
The RAMpocalypse may be the precursor to the AIpocalypse
Bots, not people, are now the ones who use the internet the most

The jscrambler npm package was compromised, and simply installing its 8.14.0 release runs an infostealer on your machine. Published on July 11, 2026, the malicious version carries …

Cybersecurity researchers have disclosed details of sustained cyber espionage activity against several Pakistani law enforcement organizations undertaken by suspected China- and In…
Multiple campaigns are using ghost accounts to map GitHub organizations, including their repositories and members. The post Ghost Accounts Abuse GitHub API in Mass Recon Campaign a…
The Australian Cyber Security Centre (ACSC) issued an alert about a global exploitation campaign targeting vulnerable content management systems (CMS) and plugins. [...]
OpenAI and Anthropic have built AI Swiss Army Knives, but the future may be smaller built-for-purpose tools
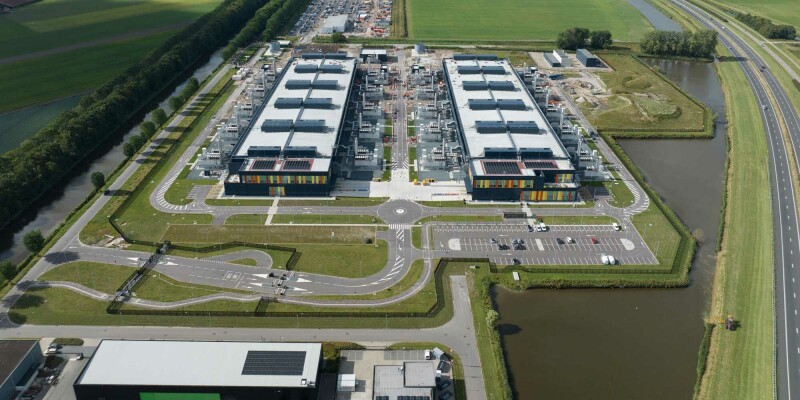
Consumption rose another 10% while restrictions on most new grid connections remained around Dublin
A PNG hiding a prompt injection could steal your repo's secrets, researchers demonstrate. The technique, dubbed 'Ghostcommit,' slipped past AI code reviewers CodeRabbit and Bugbot,…