ASOS Breach Reveals the Risks in Customer-Facing SaaS
The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network.
Aggregated from vendor advisories, security research, and industry publications.
The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network.
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters…
The ChatGPT maker said the researchers "violated clear policies on handling sensitive information.” The post OpenAI Fires 3 Safety Researchers in Dispute Over AI Risks appeared fi…
Hackers are abusing legitimate Bing search-result redirects as click URLs in Google search ads to direct users to fake Claude installers that deliver ClickFix attacks. [...]
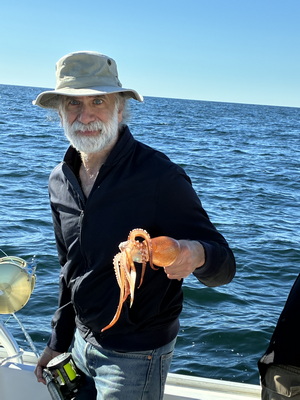
On Wednesday I spent a day fishing, on a small boat out of Gloucester, MA. We caught many cod (none of which we could keep), and a bunch of hake and mackerel (all of which we could…
Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What's different: Many of the buyers are not your typical cy…
For the first time in 14 years, the internet is getting a ton more generic Top Level Domains (gTLDs). When the internet’s domain system started back in 1985, there were only a f…
Tokens transmitted in metadata, weak VM isolation, and expansive permissions make hacking a lot easier

Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious w…

The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in S…
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the arrest of a suspected ShinyHunters operative to the compromise…
Threat actors are exploiting one critical and one medium-severity vulnerability still unpatched in the AhsayCBS backup management platform to deploy webshells and cryptocurrency mi…
The FBI has arrested another suspected member of the ShinyHunters extortion group believed to be involved in the recent breach of FBI systems, Director Kash Patel announced Friday.…

Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variants we usually observ…
Those closest to executives must match their security postures because the weakest link in a family can become the entry point for attacks.
What Microsoft giveth, Microsoft taketh away, again and again
Oracle has reportedly signed a five-year, $7 billion agreement to provide Chinese technology conglomerate Tencent with access to roughly 100,000 advanced AI accelerators deployed i…
What if the three remaining hard disk manufacturers became two? Seagate Technology and Western Digital control 90% of the market, according to market researcher TrendForce, with To…
Low-band frequencies can reach devices inside buildings, while 2 GHz orbiters could extend coverage beyond cell towers
Germany has arrested a Russian national suspected of being a leading member of the Qilin ransomware group following extradition from Japan earlier this month. [...]
Christian Adell and David Flores join host Scott Robohn to discuss the intersection of observability, automation, and networking in AI data centers. With AI data centers linking th…
SPONSORED FEATURE: While linking the GPUs in a datacenter is a challenge, coordinating thousands of them to work efficiently over hundreds of kilometers presents a new set of diffi…
Bart Dorlandt discusses the practical applications and architecture of the BGP Monitoring Protocol (BMP) for service providers. Bart has developed a BMP application to help his cus…
Analysts welcome Fusion Claw's tighter controls but warn of early adoption and cloud lock-in
For the third week running, Citrix has issued a critical security warning to customers managing their own NetScaler ADC and Netscaler Gateway instances, this time warning of a memo…
AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains h…
Buyers rushed to beat hikes earlier this year, but demand has since dried up as AI-fueled component shortages send costs soaring

Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege …
As AI agents gain authority over business systems, attackers can manipulate them like business email compromise (BEC) victims.

Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone appro…