Cisco searched for IOS XR bugs and found so many it rolled them into an update release
Three critical vulns demand your attention, one a make-me-root mess in Nexus 9000 Series Switches that you can mitigate, not fix
Aggregated from vendor advisories, security research, and industry publications.
Three critical vulns demand your attention, one a make-me-root mess in Nexus 9000 Series Switches that you can mitigate, not fix
Demand for AI, networking, and servers drove HPE to a record quarter, the company reported during its third-quarter earnings call with financial analysts. “AI has become a multi…
Daybreak program brings subsidized models, training, and support to under-resourced teams
OpenAI slow-walks debut of delayed GPT-6, with Trusted Access Program participants getting first shot
$12.9 billion deal will inevitably cement Nvidia's market dominance and harm competition in the process. Regulators should take note
France's data protection authority (CNIL) has fined Hôpital privé de la Loire €500,000 ($580,000) for failing to adequately protect patients' and their relatives' data. [...]
Threat actors behind the "Phantom Deal" campaign are studying companies in extreme detail, aiming to dupe midlevel employees into initiating large financial transfers.
Software-defined networking (SDN) and virtual networking have long been part of VMware’s portfolio, notably with the NSX technology that’s a foundational part of VMware Cloud Found…
Attackers compromised Coder's Cloudflare infrastructure and added unauthorized registry servers that delivered malicious Terraform modules containing credential-stealing code. [...…
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the latest antics of ShinyHunters to new research about the preval…
Hewlett Packard Enterprise (HPE) has patched a critical vulnerability in the ArubaOS-CX network operating system that could lead to remote code execution. [...]
All three are recovering from overlapping availability issues
A shared security 'Nightmare'

The worst part is how normal these attacks look. A call from IT. A shared file. A trusted app. A simple request to click “Allow.” Why break in when someone might open the door? Th…
Prompted by CentOS 8's premature demise, it's a very visible loss for the Red Hat ecosystem
Is your current network monitoring infrastructure capable of seeing IPv6 traffic or are you flying blind in a dual-stack environment? Today Ed, Nick, and Tom explore the critical c…
Ethan and Holly tackle the Link Layer Discovery Protocol (LLDP). They explain how this protocol helps network engineers map network topologies and validate wiring. They also discus…
When the moon is in the seventh house...
The recent open letter is right about the "window," but it omits naming who is coming through it or, critically, who will close it.
The FOSS tool for audio editing has a fresh coat of paint, and new features to boot
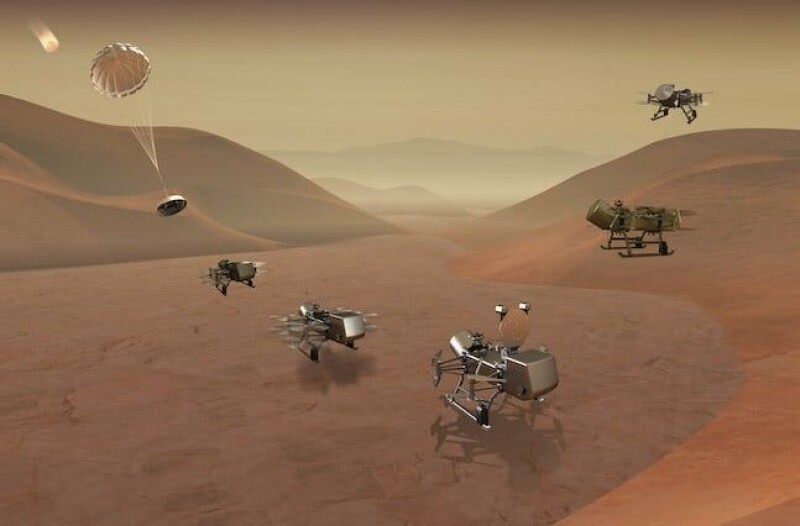
Titan-bound rotorcraft set for launch in 2028

Cisco has released patches to address a critical security flaw affecting 10 Silicon One-based Nexus 9000 switches that could allow an unauthenticated, remote attacker to execute co…
Hacker group published roughly 550GB of data after MAG reportedly refused to pay a ransom demand; the group says it gained access via exposed admin keys. The post Manchester Airpor…

Cybersecurity researchers have disclosed details of a sophisticated Python-based Windows malware framework called BraZetsu that fuels an underground marketplace commercializing acc…
Microsoft says a known issue that reverts mouse settings after installing the KB5120998 August 2026 preview update affects only non-English Windows 11 systems. [...]
New models, trained using NVIDIA Nemotron 3 Ultra, aim to catch rogue agent behavior before it executes, without the latency of large-model review. The post Capsule Security Launch…
ChatGPT and Codex are experiencing a major outage, with users reporting errors across nearly every major ChatGPT feature. [...]
Claude is experiencing an outage, with users encountering elevated errors when sending requests to multiple Anthropic AI models. [...]
SPONSORED FEATURE: Boards want to know if they're less exposed than last quarter. Patching metrics aren't the solution
A recently patched critical vulnerability (CVE-2026-32475) in the Elementor Pro plugin for WordPress is being exploited in attacks that deliver a webshell payload and execute arbit…