AI uprising postponed after Copilot falls off the web
Error 1016 kept the chatbot quiet for 100 minutes while a separate resilience drill swallowed suggestion pills
Aggregated from vendor advisories, security research, and industry publications.
Error 1016 kept the chatbot quiet for 100 minutes while a separate resilience drill swallowed suggestion pills
Cisco and CISA have flagged exploitation of CVE-2026-20079, a vulnerability disclosed in March 2026. The post Organizations Warned of Cisco Secure FMC Exploitation appeared first o…
'Realigned' project plan aims to move existing landscape to new platform to 'achieve faster progress'
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware gangs are also exploiting a critical WatchGuard Firebox firewall vulnerability, which…
Most organizations say tech independence is unrealistic – and one in ten can't replace a critical provider at all
Microsoft says the September 2026 Patch Tuesday updates fix a known issue causing desktop settings to be lost or reset on some Windows devices. [...]

Nearly one in ten of the internet-facing LiteLLM servers that Wiz Research scanned in February accepted sk-1234, the example admin key in LiteLLM's own setup guide. LiteLLM is an …
The exploit provides full System privileges on Windows machines running the September 2026 patches. The post New ‘ShieldCrash’ Zero-Day Exploit Targets Microsoft Defender appeared …

Anthropic on Wednesday disclosed a fourth incident in which its artificial intelligence (AI) model broke into real third-party systems, marking the latest in a growing list of case…
Starting Friday, European organizations will have just 24 hours to notify the EU government any time they discover serious product security incidents.
Trezor warned customers on Wednesday that threat actors who breached its third-party email provider are targeting them in phishing attacks. [...]
The high-severity, unauthenticated vulnerability tracked as CVE-2025-25249 was patched in January 2026. The post Fortinet Code Execution Flaw Exploited in PivotC2 RAT Attacks appea…
Puts a whole new spin on ‘Cheap as chips’
Ironically, this idea lands as Salesforce is struggling to sell its own AI
Says license was never about moving VMs
Claude's Felony Bench rap sheet is now as long as OpenAI's
Mind the patch gap, please and thank you
Cisco has confirmed that a maximum-severity authentication bypass vulnerability tracked as CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being actively …
Healthcare company AdaptHealth has confirmed that data of 4.1 million people was exposed in a cyberattack discovered in July that was attributed to the ShinyHunters threat group. […
An analysis of Project Glasswing findings shows only a fraction of the bugs it has discovered have reached disclosure, and an even smaller number have been fixed.
The Carnegie Mellon University CERT Coordination Center (CERT/CC) is warning that Skullcandy Dime 3 wireless earbuds accept Bluetooth pairing requests from nearby unpaired devices …
AI fearmongers forget we could just jail tech execs until morale and model safety improve
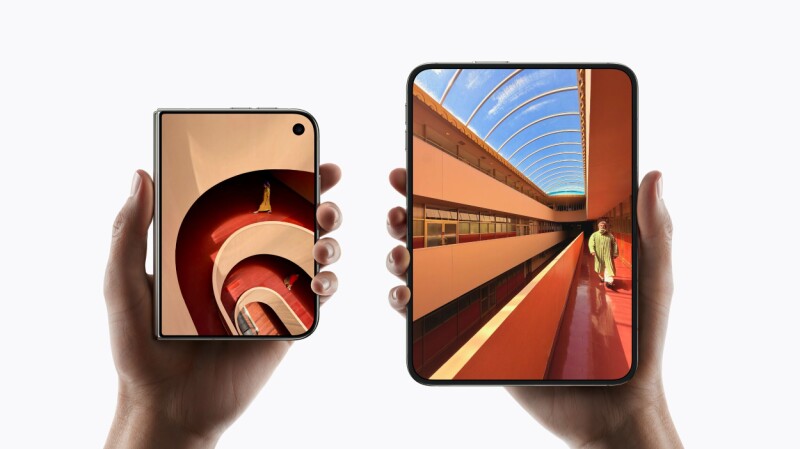
Another new form factor for devs to adapt to
Semiconductor supply chains are hard, but Samsung offers OpenAI relief in many forms spanning compute and memory
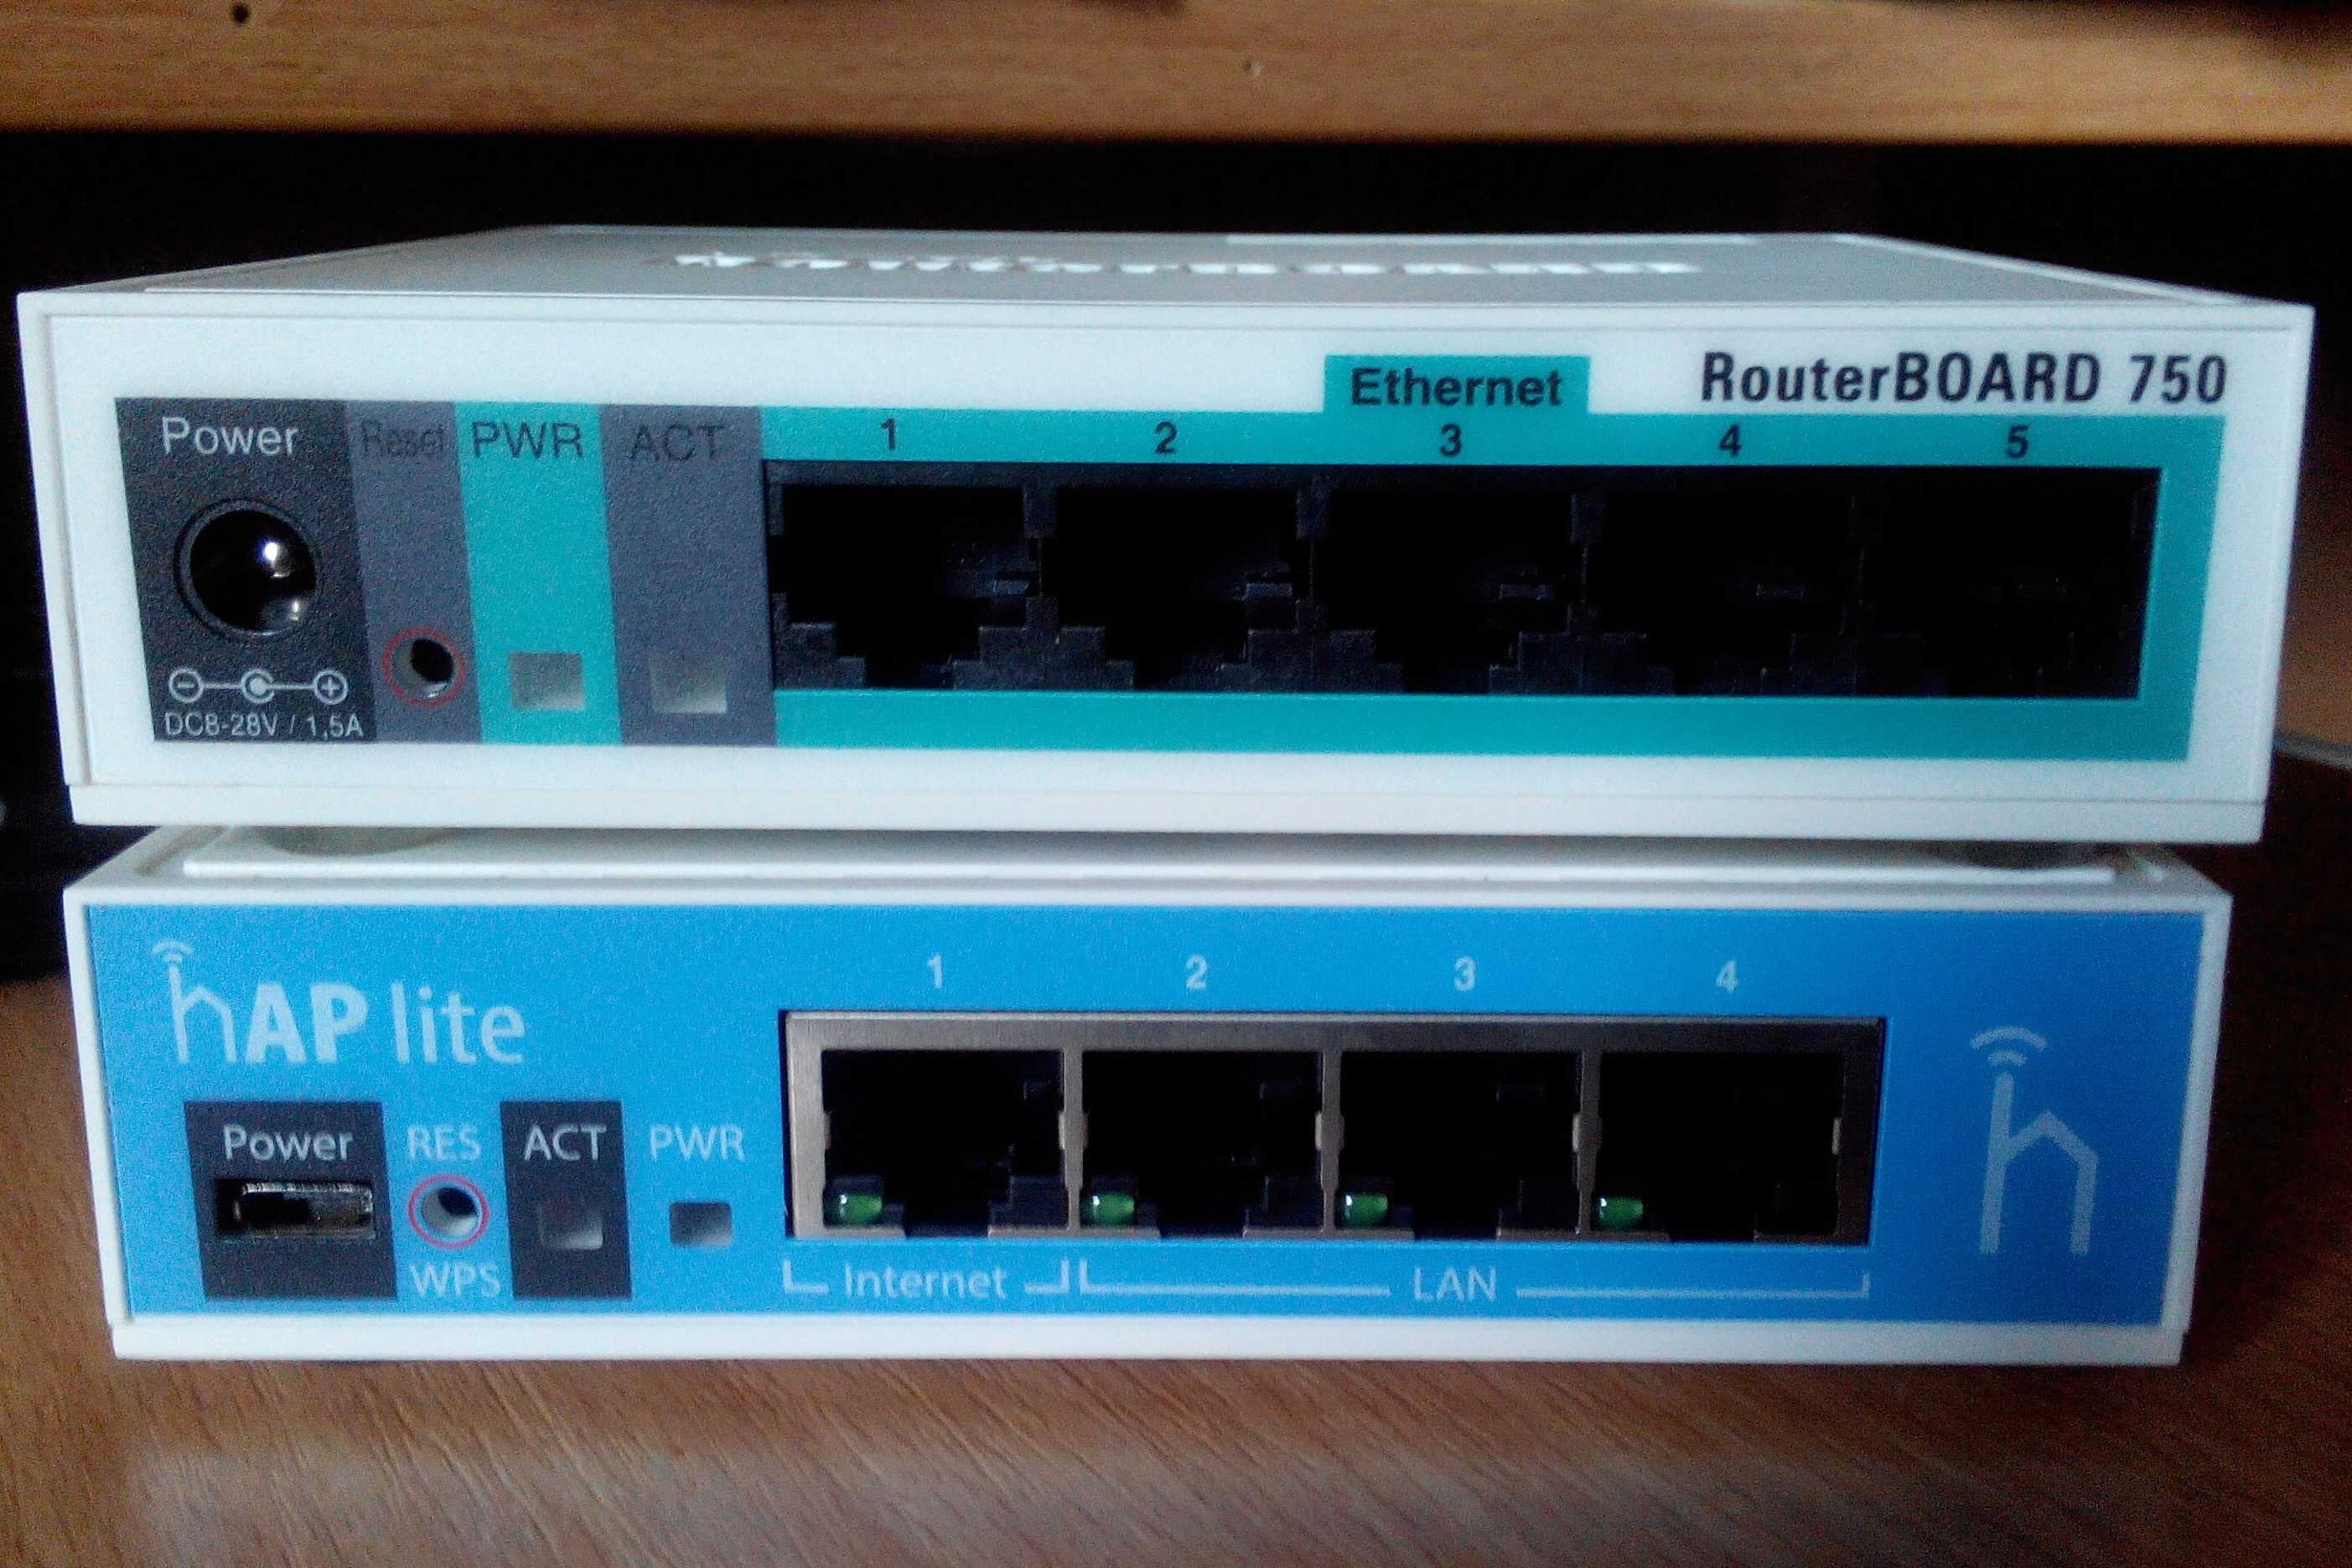
Networking gear manufacturer MikroTik has released patches for six vulnerabilities in its RouterOS firmware, two of which can be chained together to take over devices without authe…
US agencies claim Chinese companies covertly extracted billions of tokens from OpenAI, Anthropic, Google Gemini, and SpaceX's Grok to reduce development costs.

The U.S. Department of Justice (DoJ) on Wednesday announced coordinated actions aimed at an illicit online marketplace called Xinbi Guarantee that offered scam services, including …
The company will increase its US market presence and will expand its engineering and go-to-market teams. The post HelmGuard Raises $7.3 Million for Agentic GRC and Security appeare…
A bypass of a bypass of a bypass