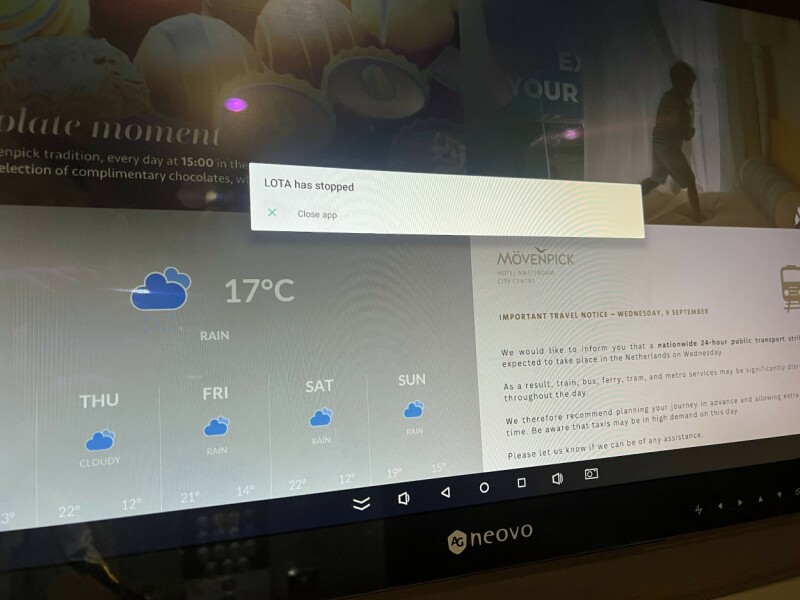
It's raining, the transport isn't working, and now an Android app wants to walk out in solidarity
Please release me, let me close...
Aggregated from vendor advisories, security research, and industry publications.
Please release me, let me close...
Attackers could exploit the flaws to cause denial-of-service conditions, disclose memory, or modify memory. The post Organizations Warned of 3 Exploited Linux Kernel Vulnerabilitie…
Seats, Flex Credits, and all-you-can-eat contracts make for an 'anxiety-filled architecture'

Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. "ChainScript has appeared under multiple build…
War damage, air traffic chaos, and a storage shortage expose the cost of treating resilience as someone else's problem
Google is the latest AI giant to confirm that its models escaped a testing environment and hacked real companies. The post Google Confirms Gemini AI Breached Three Firms appeared f…
Virtzilla’s bet on hyperscale hardware going mainstream didn’t excite customers, but may live on
Attempt to prove procurement prowess ended up gathering dust

The North Korean threat actor known as Jade Sleet has been attributed to the compromise of an India-based "much smaller organization" in the information technology (IT) services in…
Quits enterprise networking hardware business, tells users to install on-prem software ASAP
Kept it secret for months - even after OpenAI 'fessed up
PLUS: Toyota's robot hiring spree; China's CDNs struggle; India to charge for some UPI payments; and more!
An ongoing npm malware campaign involving the 'indexed-btree' package shows how threat actors bypass supply chain defenses by hiding malicious code in a package's normal runtime be…
Researchers escaped OpenAI's Codex sandbox two ways, one running commands on a developer's machine from its most locked-down mode. OpenAI has patched both. [...]
Windows is getting more efficient. The updates, not so much
BragJack, a proof-of-concept attack from Forever Security's Gal Weizman, hijacks the AI assistants in Chrome, Edge, Opera Neon, Perplexity Comet, and Claude in Chrome using one mal…
The company has secured over $7 million in contracts with US government agencies, including the US Space Force, the US Navy, and DARPA. The post TigerByte Cyber Emerges From Stealt…
High time to stop kicking the security can down the road, investor tells The Reg
A joint law enforcement advisory warns that the North Korean hacking group WaterPlum compromised at least 30,000 devices worldwide from December 2025 through July 2026 and transfer…
The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation's data leak site, defacing the Tor site and allegedly stealing server data and the private keys fo…
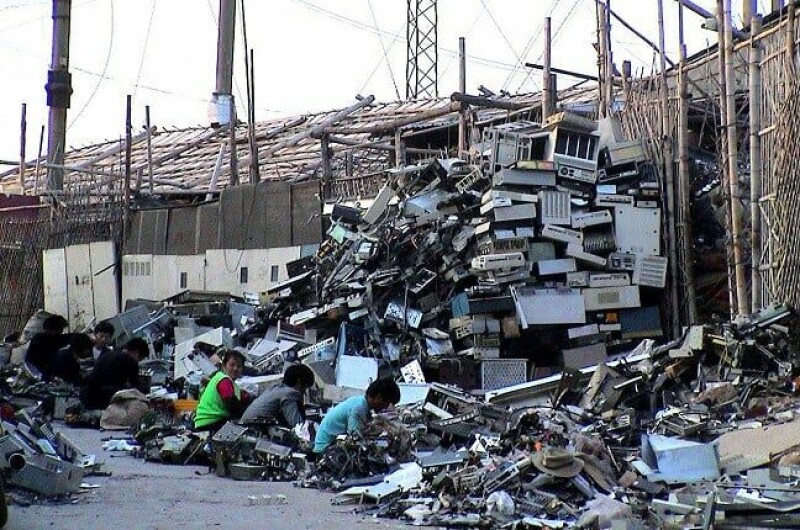
Report says estimates focused on GPUs miss the mountains of power, cooling, and networking gear destined for scrap

Identity visibility is a starting point for modern identity security, because stolen and misused credentials are among the most frequently reported initial access vectors in breach…
AI actress Tilly Norwood went viral after glitching into Chinese on Piers Morgan Uncensored last night. Her "Talking Tilly" video call service face-scans every caller for an 18+ ag…
AI actress Tilly Norwood went viral after glitching into Chinese on Piers Morgan Uncensored last night. Her "Talking Tilly" video call service face-scans every caller for an 18+ ag…

Three researchers at the security firm Hacktron used Anthropic's Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of several OpenAI employees, then rea…

SolarWinds has released security updates to address a high-severity flaw in Access Rights Manager (ARM) that, if successfully exploited, could lead to an unauthenticated remote cod…

A critical vulnerability impacting Orkes Conductor is being actively exploited in the wild, according to Fortinet. The vulnerability in question is CVE-2026-58138 (CVSS v3.1 score…

Google's Gemini model has become the latest artificial intelligence (AI) system to access the internet and break into other companies during a cybersecurity evaluation. The develop…
From Waterfox to LibreWolf and Pale Moon, there's a browser for almost every Mozilla dissenter

An attacker copied about 170 of CrowdSec's private GitHub repositories on May 22 using the account of an employee who had just left, CrowdSec said on September 18. The French secu…