For MariaDB, LLMs are the new search engines to win over
Its vector search is ready, but coding assistants keep pointing developers toward other databases, says the foundation's chairman
Aggregated from vendor advisories, security research, and industry publications.
Its vector search is ready, but coding assistants keep pointing developers toward other databases, says the foundation's chairman
The vulnerabilities, tracked as CVE-2026-28324 and CVE-2026-28325, can be exploited without authentication. The post SolarWinds Patches Critical RCE Flaws in Observability Self-Hos…
Hackers impersonated the company’s personnel and contacted its employees to gain access to Astrana Health’s servers. The post Astrana Health Data Breach Impacts Private, Confidenti…
OpenAI agents targeted public data providers in multiple countries, probing some for vulnerabilities and exploiting a security weakness in an Australian government portal while per…
For the German vendor, greater challenges may lie ahead, as rivals seek to control the user experience

ClickFix has become the most common way attackers get into enterprise networks, and it does it without an exploit, an attachment, or a file on disk. Our new global threat report tr…
Karen Vardanyan has also been ordered to pay over $1.2 million in restitution to victims. The post US Court Sentences Armenian Man to Prison for Ryuk Ransomware Attacks appeared fi…
IT took a shortcut when the boss was away, and it led to danger!
Microsoft has fixed a known issue that breaks the built-in File History backup feature on some Windows systems after installing the September 2026 security updates. [...]
Tracked as CVE-2026-87902, the path traversal flaw allows remote, unauthenticated attackers to execute arbitrary code. The post Critical WordPress Vulnerability Exploited Immediate…

An AI agent on an internal OpenAI research task bypassed access controls on an Australian government Medicare statistics portal in June, Prime Minister Anthony Albanese said. The …

Cybersecurity researchers have disclosed details of an active TeamFiltration campaign codenamed UNK_CondorFiltration that has targeted over 5,700 accounts across 28 Microsoft 365 t…

Threat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure. The vulnerability in question is CVE-2026-87902 (CVSS score: …
RIPE NCC hopes members get aboard effort to tidy things up and give its CEO a vote
Software product development industry shrinks a little, but if AI has dented prospects, it’s not in these numbers
First LLM to pass test did it in a parking lot at snail's pace, at considerable expense, but it still counts for something
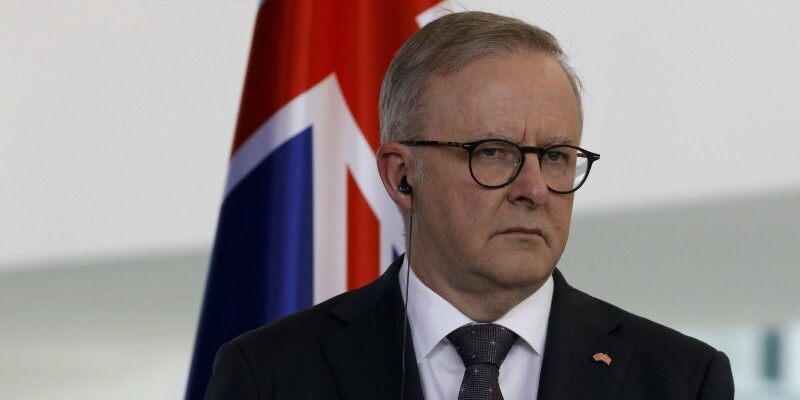
Canberra is fuming after AI lab sent the news to a generic unattended email address
The "third-party.com" domain, commonly used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that attempts to trick Win…
Enterprise computing is moving to the edge. Keeping it secure requires tactics far beyond putting up firewalls. (Second in a three-part series.)
A new Android malware-as-a-service (MaaS) platform called RemControl is targeting users through malvertising campaigns that impersonate the TVTap IPTV application. [...]
A process parameter-poisoning technique evades EDR by injecting code into process initialization structures without using the Windows APIs that EDR tools typically watch out for.
Incoming email addresses automatically assigned to each user on the platform contain highly privileged access tokens that attackers can use.
Technology company F5 fixed a critical remote code execution vulnerability in its BIG-IP Access Policy Manager (APM) platform on Tuesday. The flaw impacts deployments configured as…
Jev-powered Slop Mop demonstrates another great use case for probabilistic, non-chatty AI model
Cybersecurity company Check Point has confirmed active exploitation of CVE-2026-85102, a pre-authentication remote code execution (RCE) vulnerability in the VPN certificate-handlin…
IonQ’s new single processor quantum error decoder minimizes the classical computing overhead in quantum error correction. The post IonQ Targets Quantum Error-Correction Bottleneck …
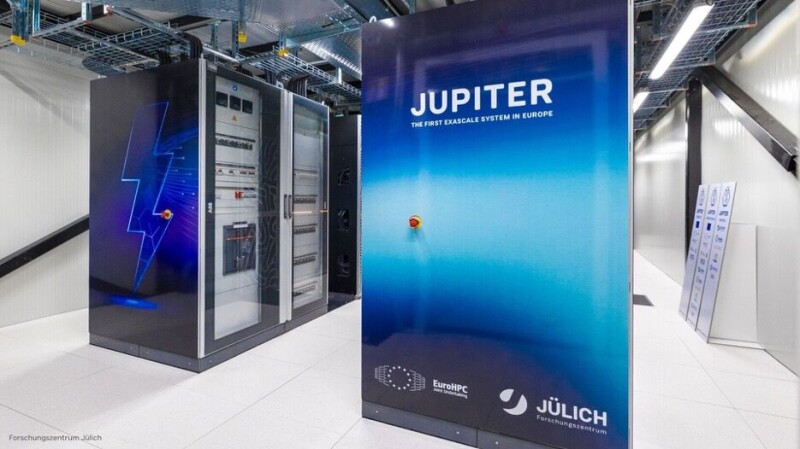
Bull, the system builder behind JUPITER, takes delivery of SiPearl's long-awaited Rhea1 CPUs
Threat actors have moved from probing WordPress sites vulnerable to CVE-2026-87902 to exploiting the flaw to write files to disk that execute shell commands when accessed. [...]
Good news: there's a patch. Bad news: both CISA and F5 warn that it's under active exploitation

Cybersecurity researchers have disclosed Go-based malware distributed via two Go Modules and two Terraform providers, marking the first time threat actors are using the centralized…