Raspberry Pi surfs memory crunch to record first half
A well-timed RAM stockpile helped keep boards shipping while rivals struggled for memory
Aggregated from vendor advisories, security research, and industry publications.
A well-timed RAM stockpile helped keep boards shipping while rivals struggled for memory
Users may need to summon Explorer manually after signing in

Cybersecurity researchers have flagged a new version of PamStealer that ensures that the main payload can only be recovered using a server-side decryption chain. The latest artifa…
The 7,000 km (4,350 mile) cable, called Petal, will connect the US and France. Meta is partnering with NEC and Sumitomo Electric Industries to build it, and working with French tel…
Justice Department claims the EU overreached by pursuing X's owner and wider corporate empire
Microsoft announced it will deprecate the Windows Deployment Services (WDS) server role starting with the next Windows Server release. [...]
Homeland Security Secretary Markwayne Mullin tasked CISA with developing the plan in July. The post CISA Election Security Plan Flags Patching Barriers, Voter Database Attacks app…
Ardit Kutleshi created and operated Rydox, which allowed miscreants to trade PII and cybercrime tools and services. The post Kosovar Owner of Rydox Marketplace Pleads Guilty in US …
Article URL: https://matduggan.com/im-tired-of-being-on-the-network/ Comments URL: https://news.ycombinator.com/item?id=49843547 Points: 144 # Comments: 160
Coding agents helped two developers build an accelerated desktop and graphics driver in weeks
A Kosovar national has pleaded guilty to operating Rydox, a large illegal online marketplace that sold stolen personal information, login credentials, credit card details, and cybe…

Security leaders keep debating whether AI will produce an entirely new class of cyberattack. The nearer change is quieter and already visible: AI has made a failed attack cheap to …
High-value goods remain tied up as merchants debate attack or platform glitch
Putting the 'om' in computing
Earlier this month, Anthropic published a long report detailing all of the Claude misuses it detected. Daniel Meissler usefully summarized the report into 117 findings. A few of th…
Researchers show that file-change notification systems can leak keystroke timing, browsing activity, and WhatsApp media events. The post Windows, Linux, Android File Notification S…
Force says public data appears untouched, but investigators looking into whether crims grabbed employee information

Cryptocurrency exchange Bitget said suspected North Korean threat actors have stolen $351.6 million from its hot and warm wallets. "At 18:31 UTC on September 24, 2026, Bitget's s…
Microsoft has confirmed that some users may experience desktop loading issues, including black screens, after installing the August 2026 preview updates and subsequent updates. [..…

The Canadian Centre for Cyber Security has warned that a now-patched Roundcube Webmail vulnerability is being actively exploited in the wild. The vulnerability in question is CVE-…
DriveWealth coughs up historic customer info after attackers socially engineer their way inside
Three vulnerabilities in Salesforce Agentforce allowed hackers to hijack trusted agents, steal data, and launch phishing attacks. The post ‘SalesBleed’ Flaws in Salesforce Agentfor…
Ohio man planted a device on a delivery van to follow scarce trading card stock and caught a year of probation
Joe Fay chairs a Register dinner on the file infrastructure nobody has got round to replacing, under the Chatham House Rule.
Cryptocurrency exchange Bitget disclosed today that suspected North Korean hackers have stolen $351.6 million from its hot and warm wallets. [...]
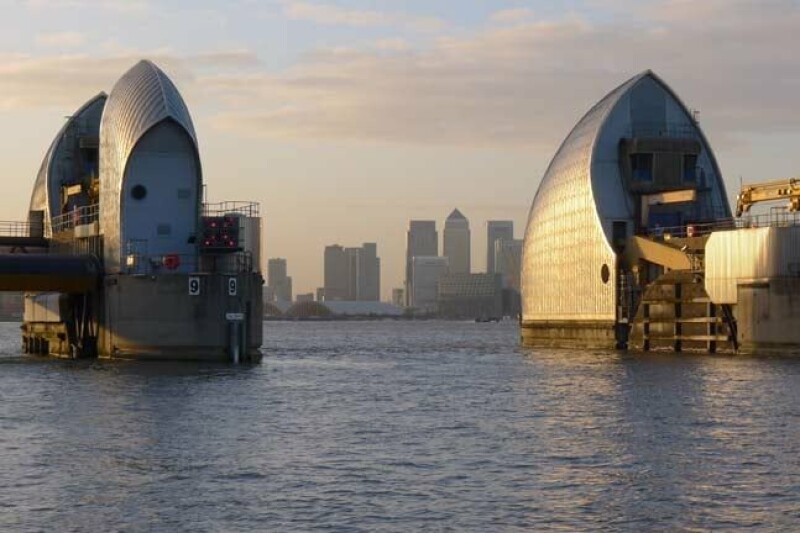
Millions for building and improving bitbarn driven heat networks - including hot water pushed through tunnel under the Thames
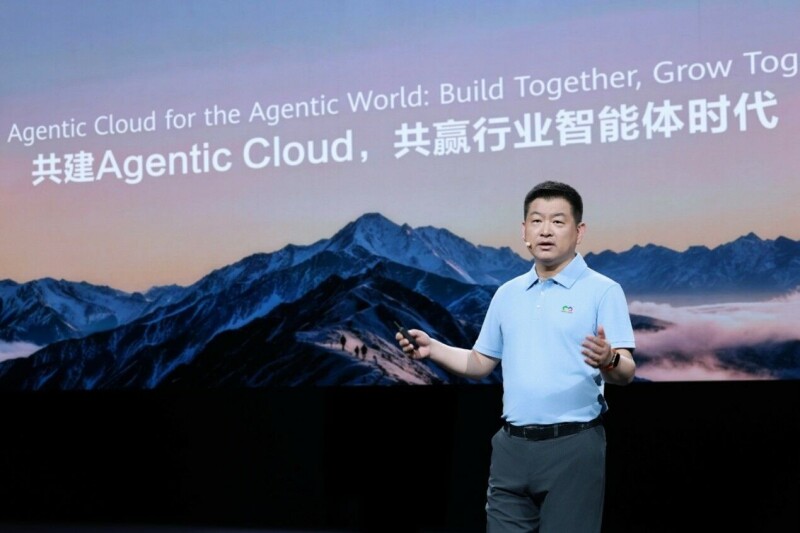
PARTNER CONTENT: Huawei Cloud strengthens the silicon bedrock on the cloud
Article URL: https://www.safateam.com/intelligence-hub/research/technical-articles/cve-2025-13032-entering-and-breaking-the-avast-antivirus-sandbox-part-2 Comments URL: https://new…
A storm is raging in the form of cyber sabotage, disinformation, and drone attacks on European nations, particularly those that provide material support to Ukraine.
Tracked as CVE-2026-48842, the exploited bug is an SQL injection that can be exploited without authentication. The post Roundcube Webmail Vulnerability in Attackers’ Crosshairs app…