OpenAI's wandering AI agents earn it a California subpoena
Plus: Attorneys-general say investigators should have direct access to AI companies' records when things go wrong
Aggregated from vendor advisories, security research, and industry publications.
Plus: Attorneys-general say investigators should have direct access to AI companies' records when things go wrong
Noteworthy stories that might have slipped under the radar: Kiteworks patches over 100 vulnerabilities, Microsoft publishes 2026 Digital Defense Report, AI finds 24 Android app fla…
Browser-based attacks can steal sessions, abuse extensions, or manipulate users without creating the endpoint artifacts EDR is designed to detect. NordLayer explains three ways att…
Organizations don't need better vulnerability scanners; they need to know who owns their assets, and who has the authority and capacity to actually fix them.
Grid connection awaits regulatory approval, putting planned 2027 customer delivery at risk
Bob, IBM’s agentic software development platform is now available to run on premises and in private clouds, sovereign clouds, and air-gapped environments to give users more control…
The dropper “carries a complete universal Mach-O inside itself, roughly 756 KB in the development build, and extracts it at runtime. The post macOS Users Targeted by Fake Zoom Inst…
Two safety researchers and a program manager dismissed, company denies retaliation for raising concerns
Meanwhile 128 GB version jumps to $6,950, nearly 75% above its launch price
A trio of newly discovered backdoors walk and quack like legitimate edge solutions, so it's hard to tell they're not.
Dell has patched two maximum severity vulnerabilities in the Container Storage Modules (CSM) that connect Dell enterprise storage arrays to Kubernetes environments. [...]
Copilot builds charts and metrics from spreadsheet data, with automatic refreshes when the numbers change

OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. "We have par…
Hackers used the account, which has 13 million followers, to amplify a Clippy-themed cryptocurrency account. The post Crypto Scammers Hijack Microsoft’s Official X Account appeared…
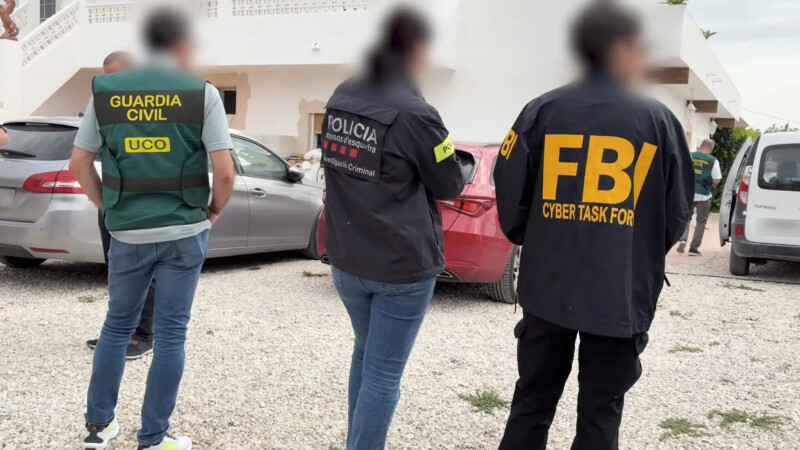
Operation KillSwitch takes over leak site holding at least 110 TB of stolen data

The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the E…
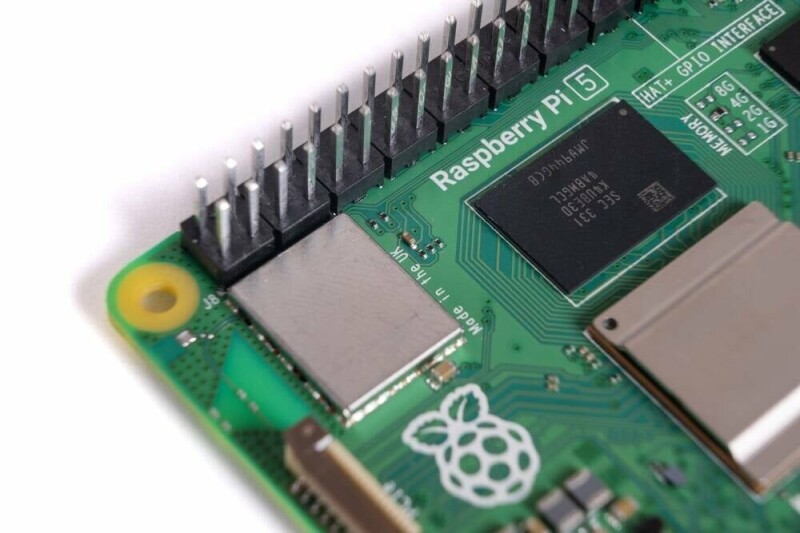
Pi 5 also gets a $12.50 bump as customers urged to consider older models or less RAM
Amir Barati, an alleged member of the Mabna Institute, was indicted for targeting universities, private organizations, and government entities in the US and abroad. The post In Rar…
This essay was written with Nathan E. Sanders, and originally appeared in The Guardian. New campaign finance disclosure data shines a light on which US political campaigns are usin…
No login required, exploitation underway, and some admins are still waiting for patches
Outsourcer admits service remains below expectations after missed recovery deadline
The China-based hacking group has been exploiting SharePoint vulnerabilities since July 2025. The post Warlock Expands SharePoint Exploitation in Critical Infrastructure Attacks ap…
On Thursday, unknown attackers hijacked the official Microsoft account on X, which has over 13 million followers, in what appeared to be a pump-and-dump scheme promoting a crypto t…
Scotland Yard hits pause after US prosecutors trace supposedly American tech back to Moscow
Hyperscalers are rushing to build more data centers to run AI workloads — but will the AI industry ever generate enough revenue to pay for that infrastructure? Researchers at B…
The attacks targeted the US Department of Education and Library and Archives Canada, and researchers linked some agents to OpenAI. The post AI Agents Aimed SQL Injection at US and …
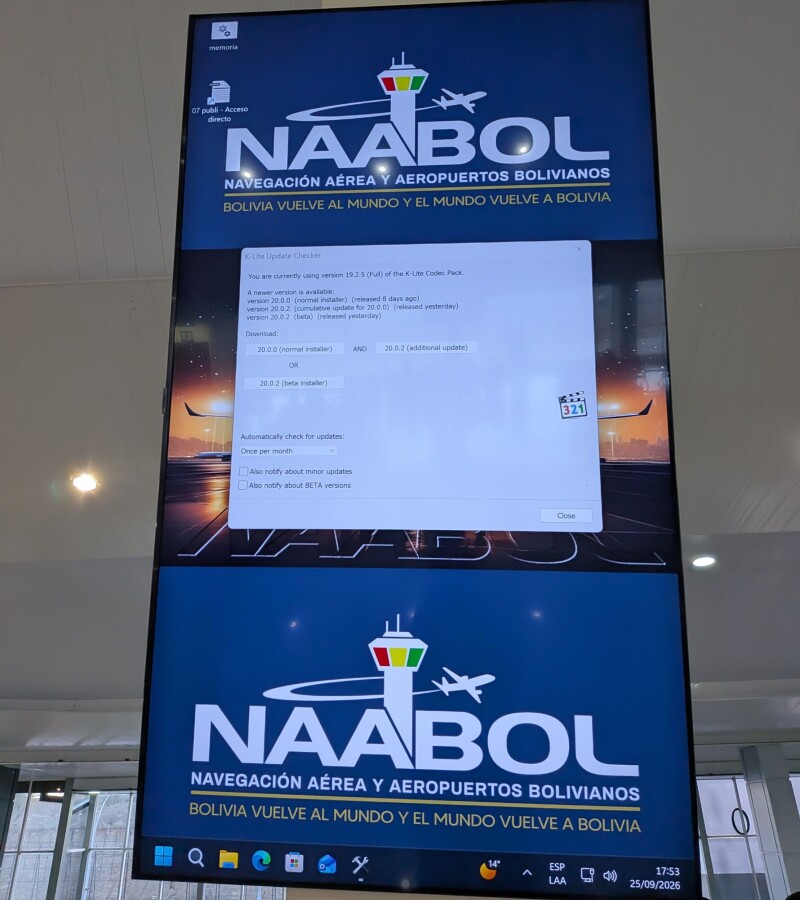
A slice of Bolivian bork at Alcantarí International Airport
CVE-2026-104286 is a critical-severity path traversal vulnerability that could allow attackers to write arbitrary files to the system. The post Exploited Fortinet FortiMail Zero-Da…

Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protecti…
Sales calls can be even nastier than support calls