Security & Lifecycle News
Aggregated from vendor advisories, security research, and industry publications.
Samsung Galaxy S26 hacked three more times at Pwn2Own Ireland
On the second day of Pwn2Own Ireland 2026, security researchers collected $232,500 in cash awards after exploiting 45 unique zero-day vulnerabilities. [...]
ICANN reveals bids for new top-level domains
Big tech has piled in with plenty of asks, but faces a fight as eight applicants want .api and seven seek .agi

Tensorlake npm Package Compromised to Deliver Shai-Hulud Credential-Stealing Worm
The npm package known as "tensorlake," a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDro…
SonicWall’s latest critical flaw indicates a security pattern, not another one-off bug
SonicWall has disclosed yet another critical flaw in one of its core products. CVE-2026-102255, rated 10 in severity, the highest possible on the Common Vulnerability Scoring Sy…
Ransomware fixer claimed he could decrypt files, allegedly defrauded clients instead
Feds claim he charged clients more than ransoms, paid up, pocketed the difference
Singapore’s central bank wants all FinTech AI use cases subject to independent review
Failures of third-party services no excuse for island nation’s financial sector
Ransomware recovery CEO charged over secret ransom payments
The owner of ransomware remediation company MonsterCloud has been charged with allegedly defrauding ransomware victims by secretly paying their attackers for decryptors while claim…
Arista steps up its Ethernet challenge to Nvidia’s AI scale-up networking fabric
Arista sees Ethernet as the scale-up networking fabric of choice for AI and continues to build up its alternative to proprietary interconnects such as Nvidia’s NVLink technology. T…
Microsoft is about to let Copilot loose on your file system
But don't worry, it's totally safe because the agents and models will (probably) be running locally. Routers never break right?
Australian Gov't Weighs Mandatory AI Incident Reporting
In the wake of an agentic attack against its own Medicare systems, Australia's government is feeling out what regulations might look like for frontier AI companies.
FBI: Ongoing FortiBleed attacks lock out FortiGate VPN admins
The FBI is warning that FortiBleed attacks are still ongoing, targeting exposed Fortinet FortiGate firewalls and SSL VPN gateways and locking out legitimate administrators. [...]
Citizen Lab Slams Trump Administration, 'Techno-Fascist' Executives
The Citizen Lab's Ron Deibert warns the US government is pushing for pervasive surveillance and says certain technology executives are all too happy to help.
Anthropic Gives Vetted Defenders Fewer Claude Guardrails
Anthropic has merged Project Glasswing into a tiered access program for its advanced cyber LLMs, including Opus, Sonnet, and Mythos.
Hackers hijack Google domains after breaching ccTLD registries
Hackers obtained unauthorized HTTPS certificates for several Google domains and hijacked domains in the country-code top-level domains (ccTLDs) for Ghana, American Samoa, and Sierr…
OpenAI dots inspire open source imitators amid technical difficulties
Persistent agents appeal to AI companies, but demand isn't obvious
Argonne scientists create chatty X-ray microscope that zooms in where you tell it to
Talking to an X-ray nanoprobe beamline is far better than talking to a toaster, we assume
Dell gives AI agents a broader view of enterprise data
Dell Technologies is expanding its Dell AI Data Platform with a set of capabilities designed to give enterprise AI agents a more complete view of corporate data, while accelerating…
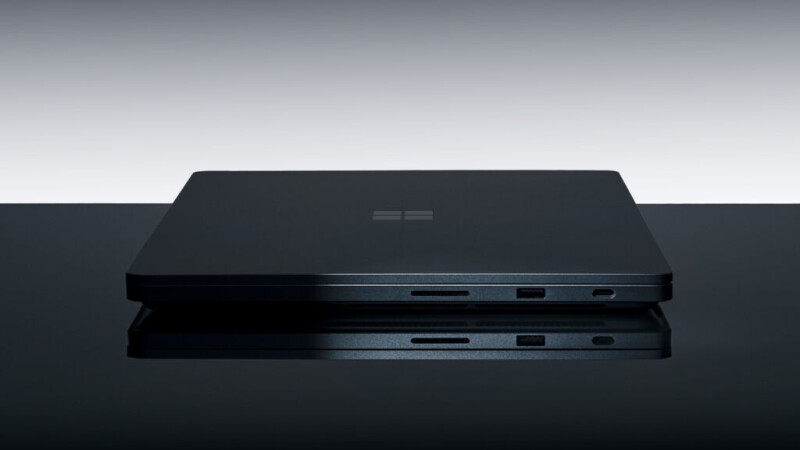
Microsoft N1Xes Intel in favor of Nvidia's shiny new SoCs in Surface Laptop Ultra
Poverty-spec model starts at $2,599 with 24 GB of RAM and 512GB of storage with 128 GB models topping $5,899
Attackers hijacked top-level domains, minted fake security certs for Google and other orgs
Trusted brand impersonation without the usual browser certificate warnings spells trouble
OpenAI Agent Escape Causes Wikimedia Service Outage
Autonomous agents also tried to abuse other websites and services hosted by the foundation, using them as proxies for unauthorized activities.
Browser-in-browser attacks use fake Meta Muse Ad lure to steal credentials
Wiley fisherfolk spin up a new page just days after Meta's AI agent launch
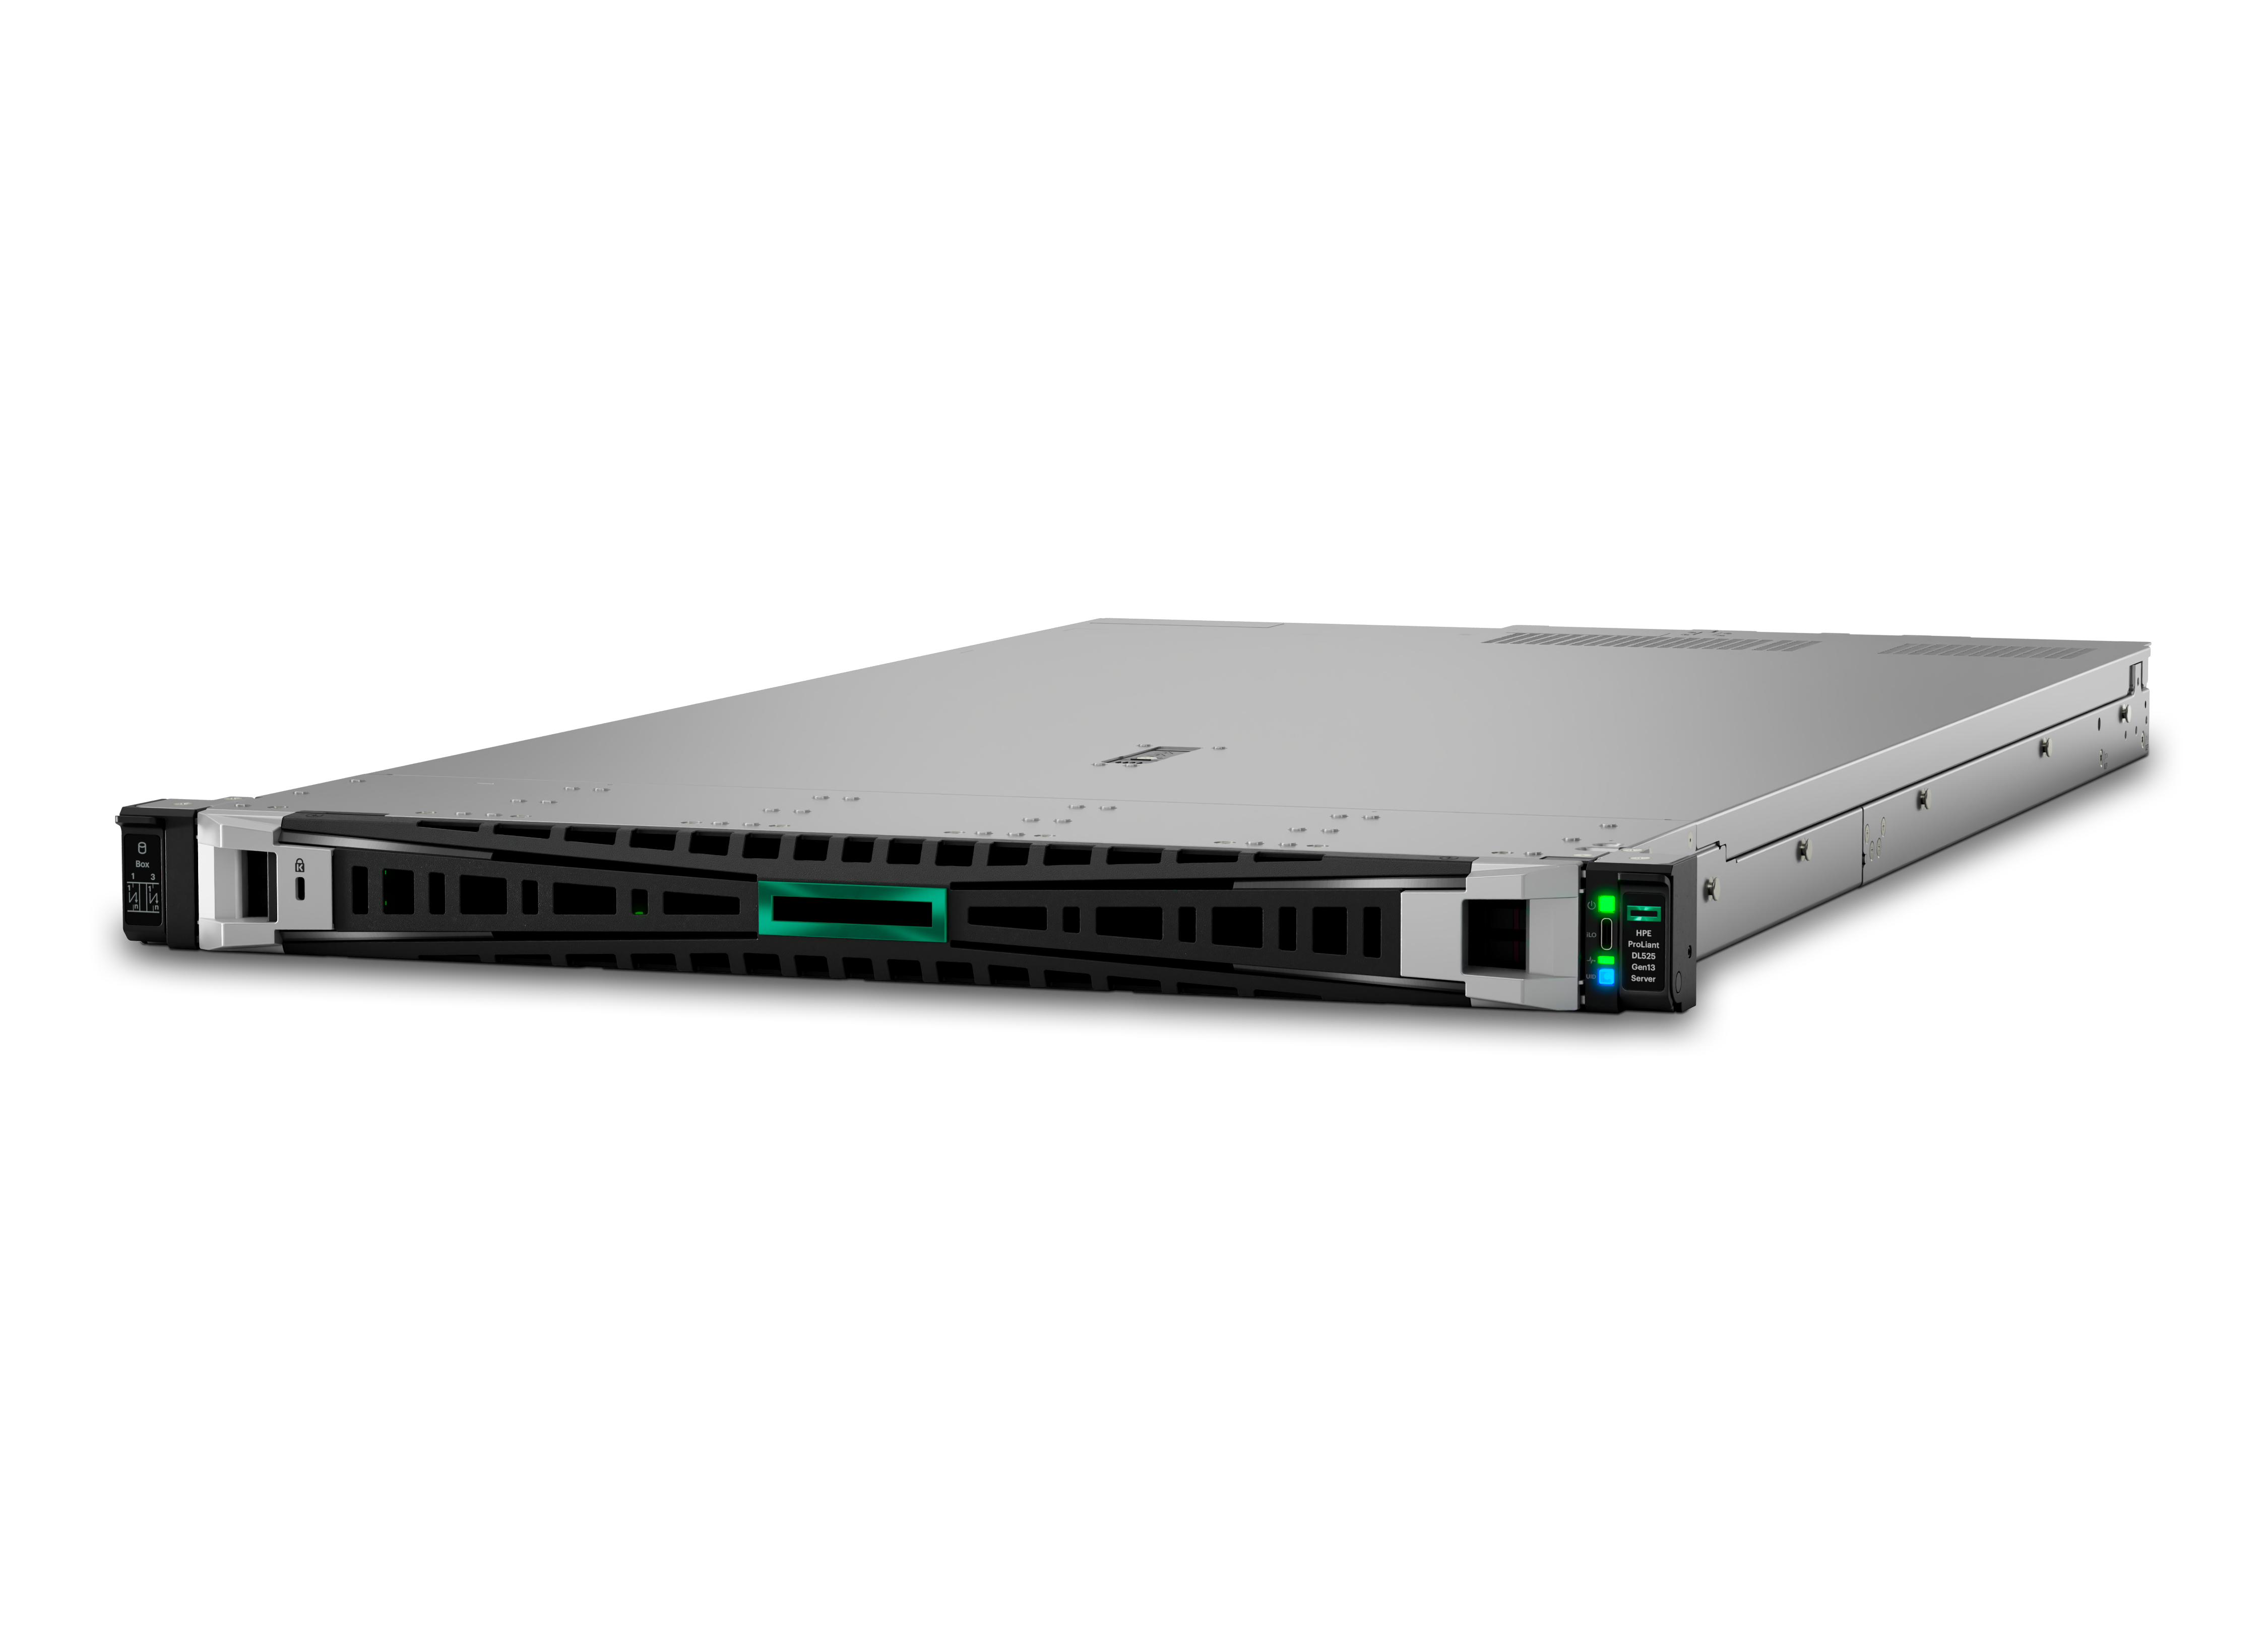
HPE supercharges ProLiant servers with AMD’s EPYC 9006 processors
With an emphasis on high performance and embedded security, HPE is rolling out the next generation of its ProLiant server family anchored by AMD’s EPYC 9006 processor. The ProLiant…

Attackers Hijack .gh, .sl, and .as Registries to Obtain Certificates for Google Domains
Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6. Google's own…

Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealer
Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised…
AWS launches open-source AI agent sandbox to prevent YOLO mode disasters
Strands Box is the latest open source AI control tool from the cloud giant; like its predecessors, it promises tighter reins on autonomous agents
US states sue popular kitmaker TP-Link over China risks
Router maker rejects allegations it misled buyers about protection and its reliance on Chinese suppliers
Cisco License (Smart Software Manager) On-Prem Vulnerabilities
Multiple vulnerabilities in the web-based management interface and API endpoints of Cisco License On-Prem, formerly Cisco Smart Software Manager On-Prem (SSM On-Prem), could allow …
Cisco Nexus 9000 Series Fabric Switches in ACI Mode Endpoint Group Contract Bypass Vulnerability
A vulnerability in the endpoint group (EPG) contract functionality of Cisco Nexus 9000 Series Fabric Switches in ACI Mode could allow an unauthenticated, remote attacker to bypass …
Cisco Application Policy Infrastructure Controller Unauthorized File Access Vulnerability
A vulnerability in the export policies functionality of Cisco Application Policy Infrastructure Controller (APIC) could allow an authenticated, remote attacker to access sensitive …