US disrupts Chinese hacking tools as 7 govts warn of PRC spies stealing sensitive data worldwide
Infecting devices from 2021 until the FBI stepped in
Aggregated from vendor advisories, security research, and industry publications.
Infecting devices from 2021 until the FBI stepped in
Commitment comes as GPUzilla prepares to fortify Uncle Sam's arsenal with at least seven AI-optimized supers
The FBI has seized seven domains used by Chinese state-sponsored hackers known as Flax Typhoon to operate two hacking tools, MicroScan and FishHub, used in attacks that breached cr…
A now-patched vulnerability in AWS Bedrock AgentCore could have allowed an attacker to use one AI chatbot to take over an organization's entire fleet.
Enterprise organizations typically use six to eight observability tools, creating integration, staffing, and visibility challenges as network operations teams adopt AI to help mana…
The Chocolate Factory proposes a single universal agent for work
Space agency claims steady progress on lunar reactor plans, but offers little evidence to back it up
IDC Frontier, a major Japanese cloud and digital infrastructure company, disclosed that its IDCF Cloud service was targeted in a ransomware attack that caused an outage at a data c…
A malware campaign dubbed 'Midnight Mimosa' has been discovered on low-cost Android smartphones that ship with malicious software embedded in their firmware, allowing attackers to …
The first cybercriminal to ever make the FBI's "10 Most Wanted Fugitives" list allegedly infused Tren de Aragua's violent criminal operations with cash.
AI clusters depend on two types of networking. Scale-up networking connects accelerators inside a rack. Scale-out networking connects racks across the data center. A single AI job …

Hackers tied to a Chinese cybersecurity company stole email from government organizations, law enforcement agencies, healthcare systems, and religious institutions in Southeast Asi…
The GPU giant released a fix for the flaw, tracked as CVE-2026-47483
Cyber-espionage actor UAC-0099 has been steadily refining its flagship dropper in campaigns targeting Ukrainian organizations.

The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools and…
Advanced packaging tech is essential to the domestic production of high-performance semiconductors used in AI datacenters
More than 17,000 fake repositories on GitHub are distributing the SmartLoader malware after the FakeGit campaign reactivated earlier this month to push the StealC infostealer. [...…
If there's one thing AI can do well, it's failing more quickly than the average SRE
Credential-stealing malware detected within minutes of npm release, but impact remains unknown
Lightyear CEO and co-founder Dennis Thankachan shares his transition from investment banking to entrepreneurship and the lessons learned from his early startup failure. He also dis…
Researchers corroborate parts of Silent Ransom Group dump detailing crypto payouts, cash brokers, and recruitment

Attackers behind a string of personal data leaks at Japanese organizations have abused APIs for mobile apps and targeted known software flaws, the JPCERT Coordination Center (JPCER…
Gartner predicts more than half will fold by 2030, even as businesses begin testing the technology's usefulness
The security defects could lead to unauthorized access, information leaks, privilege escalation, DoS attacks, and remote code execution. The post Cisco Patches a Dozen Critical Vul…

The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to …
Cisco released security advisories for five critical vulnerabilities in its NX-OS data center network operating system that could be exploited to run arbitrary code with root privi…
SPONSORED FEATURE: Old attack, new protections
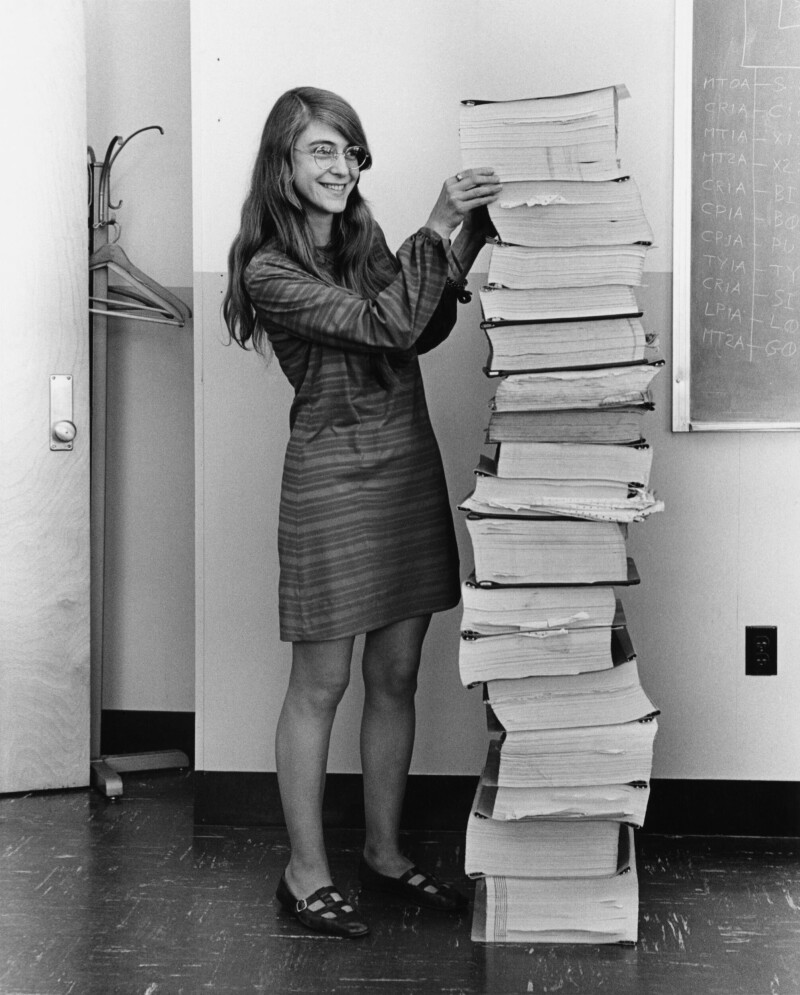
Her team's code kept Apollo 11's landing on course when the guidance computer became overloaded
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable. The post Security Awareness Training Isn’t Dead, but I…

Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool nam…