Comcast gives its Wi-Fi motion detector a security makeover
Rebranded feature promises household alerts without video, but mind the small print
Aggregated from vendor advisories, security research, and industry publications.
Rebranded feature promises household alerts without video, but mind the small print

A previously unreported cyber espionage operation dubbed SilkParasite has been observed targeting government bodies in Central Asia. The intrusion set makes use of seven remote ac…
Big Red's acquisition of MySQL sent users running toward the open source alternative, says Michael Stonebraker
The previously bootstrapped company helps organizations securely and reliably operate AI agents at scale. The post Prevalent AI Raises $22 Million to Expand Data Fabric Platform ap…
Load balancers buckled after a monitoring blind spot allowed traffic to spiral

Cybersecurity researchers at Hunt.io have disclosed details of a campaign that they say compromised more than 14,530 Dahua devices between June 17 and July 22, 2026, using credenti…
The 17 members of the Mabna Institute targeted hundreds of universities and organizations in the US and abroad. The post US Charges 17 Iranian Hackers, Offers $10 Million Rewards f…

Most email defenses still do the job they did a decade ago. Scan the message, look for something malicious, block it. That worked when the danger sat in the payload, a bad link or …

Cybersecurity researchers have flagged a global cybercrime operation that abuses thousands of hacked WordPress websites as infrastructure to disseminate malware, commandeer infecte…
Microsoft has resolved a bug that caused Windows Defender to crash after a recent security update, resulting in 0xc0000005 access violation errors on some affected systems. [...]
The cybercrime gang has listed major companies such as Shell, Philips, Fiserv, Zebra, Mindray, and Largan Precision. The post Cl0p Ransomware Group Names Over 40 Victims of PTC Win…
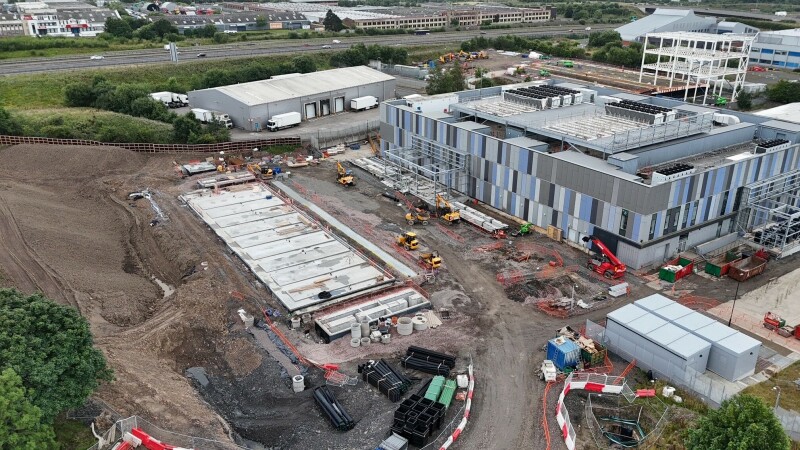
DataVita secures funding to expand datacenter capacity, while Dell brings some desks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, stating they a…
ICE collected nearly a million DNA samples last year.
The flaws can be exploited for remote code execution, authentication bypass, and device takeover. The post CISA Urges Immediate Patching of Exploited Microsoft, VMware, Apple Vulne…
Cerebras Systems has unveiled the CS-4, a new rack-scale AI system that can connect its wafer-scale processors across racks without network switches, an approach designed to reduce…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are exploiting a critical-severity remote code execution (RCE) flaw in the Windows Internet Key…
Both sides apparently start high then price in the inevitable haggle
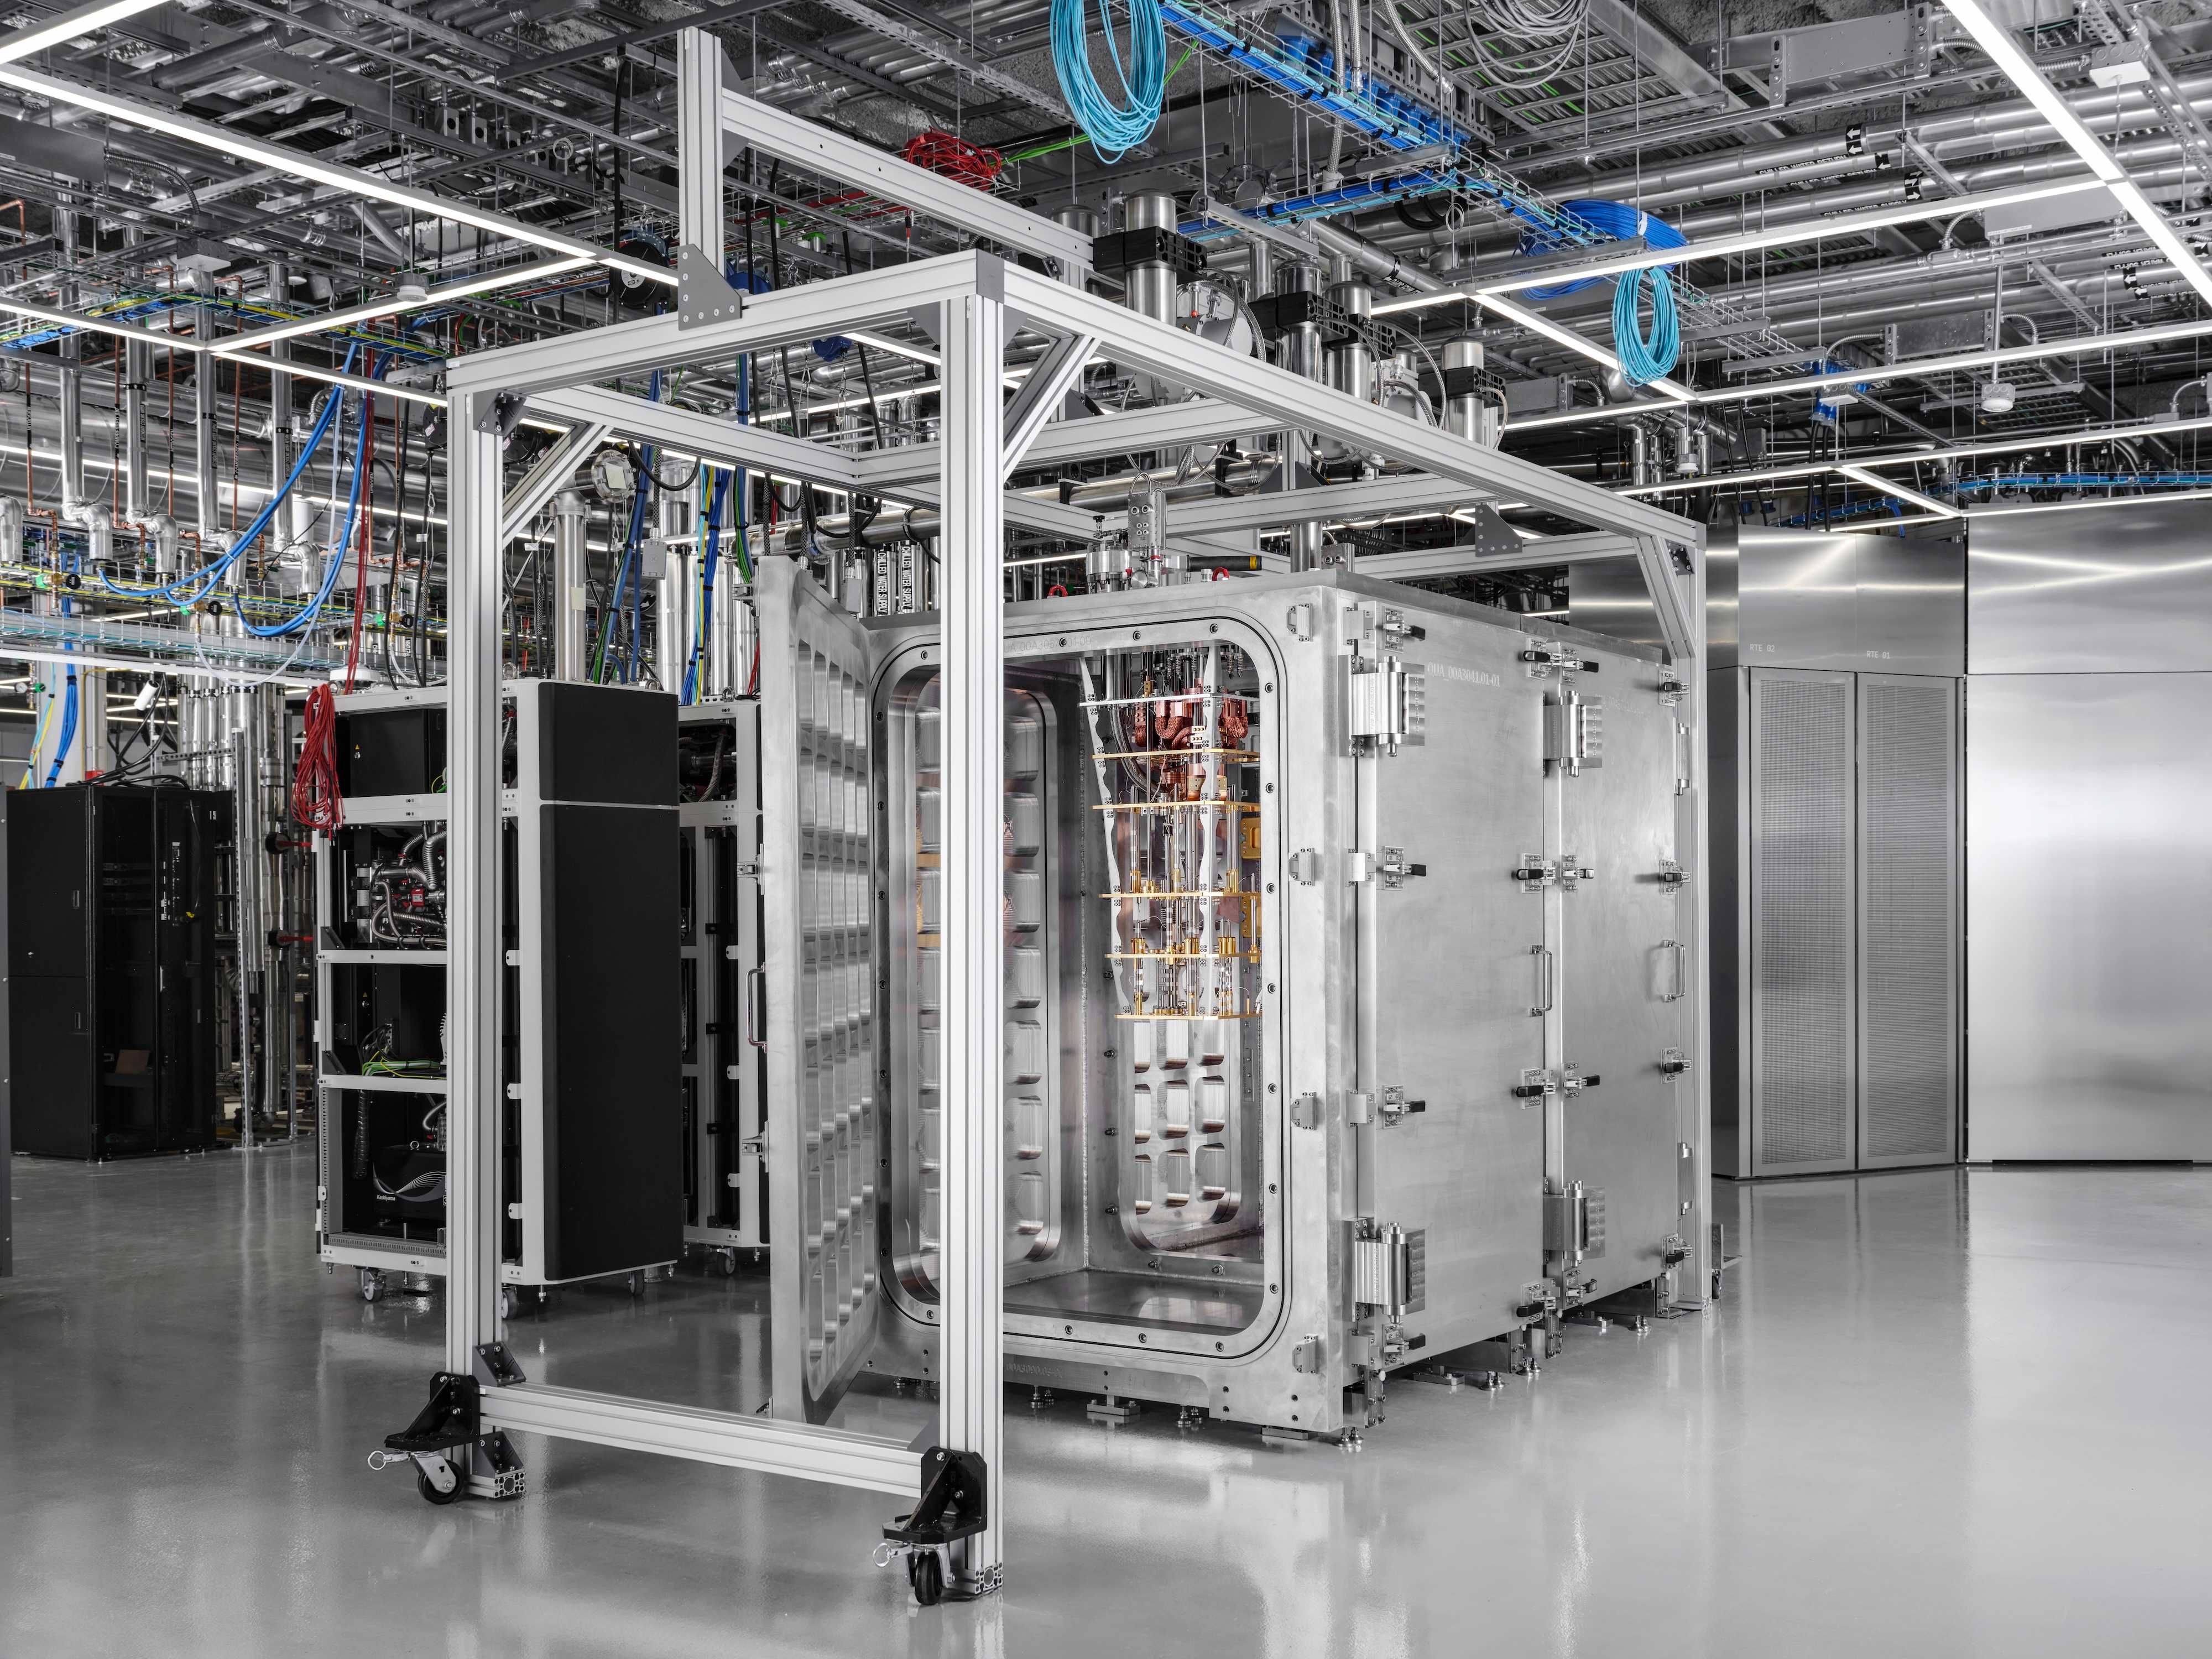
As it pursues its goal of producing a fault-tolerant quantum computer, IBM today announced that it has achieved another milestone: It has successfully joined two cryogenic modules …
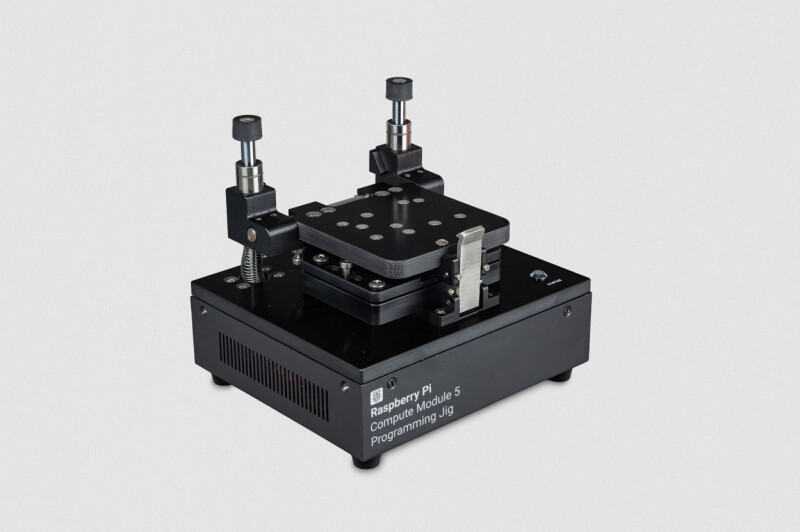
Clamp, flash, repeat – no separate IO board or host computer required
The fixes resolve over 1,000 vulnerabilities across two dozen products, including over 460 remotely exploitable bugs. The post 943 Patches Rolled Out With Oracle’s August 2026 Secu…
Microsoft has reminded customers that systems running Home and Pro editions of Windows 11 24H2 will stop receiving updates in two months. [...]
Those legacy systems won't fix themselves
The bugs could lead to code execution, privilege escalation, sandbox escape, and information disclosure. The post Chrome, Firefox Updates Patch Dozens of Vulnerabilities appeared f…
The FBI said Tuesday that the Medusa ransomware gang has breached more than 500 critical infrastructure organizations in the United States since June 2021. [...]
The data breach was initially believed to affect roughly 350,000 people, but the HHS breach tracker shows a far bigger impact. The post CareCloud Data Breach Impact Grows to 3.7 Mi…
As the latest Starship finds its way to an obscure part of Australia, for observations

Microsoft Defender Experts have linked more than 30 web domains to MacSync Stealer, a macOS-focused information stealer, after correlating recurring endpoint and network behaviors …

A JavaServer Pages (JSP) web shell deployed following the exploitation of a critical security flaw in PTC Windchill and FlexPLM servers is specifically designed for the enterprise …
It seems like Nvidia’s not getting back into the Middle Kingdom anytime soon